
Archive
21 July 2025
Vulnerabilities first published on this day (UTC), newest first.
237 results · Feed
-
Medium 6.3
fuyang_lipengjun platform ScheduleJobLogController.java queryPage sql injection
A vulnerability has been found in fuyang_lipengjun platform up to ca9aceff6902feb7b0b6bf510842aea88430796a and classified as critical. Affected by this vulnerability is the function queryPage of the file com/platform/controller/ScheduleJobLogController.java. …
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 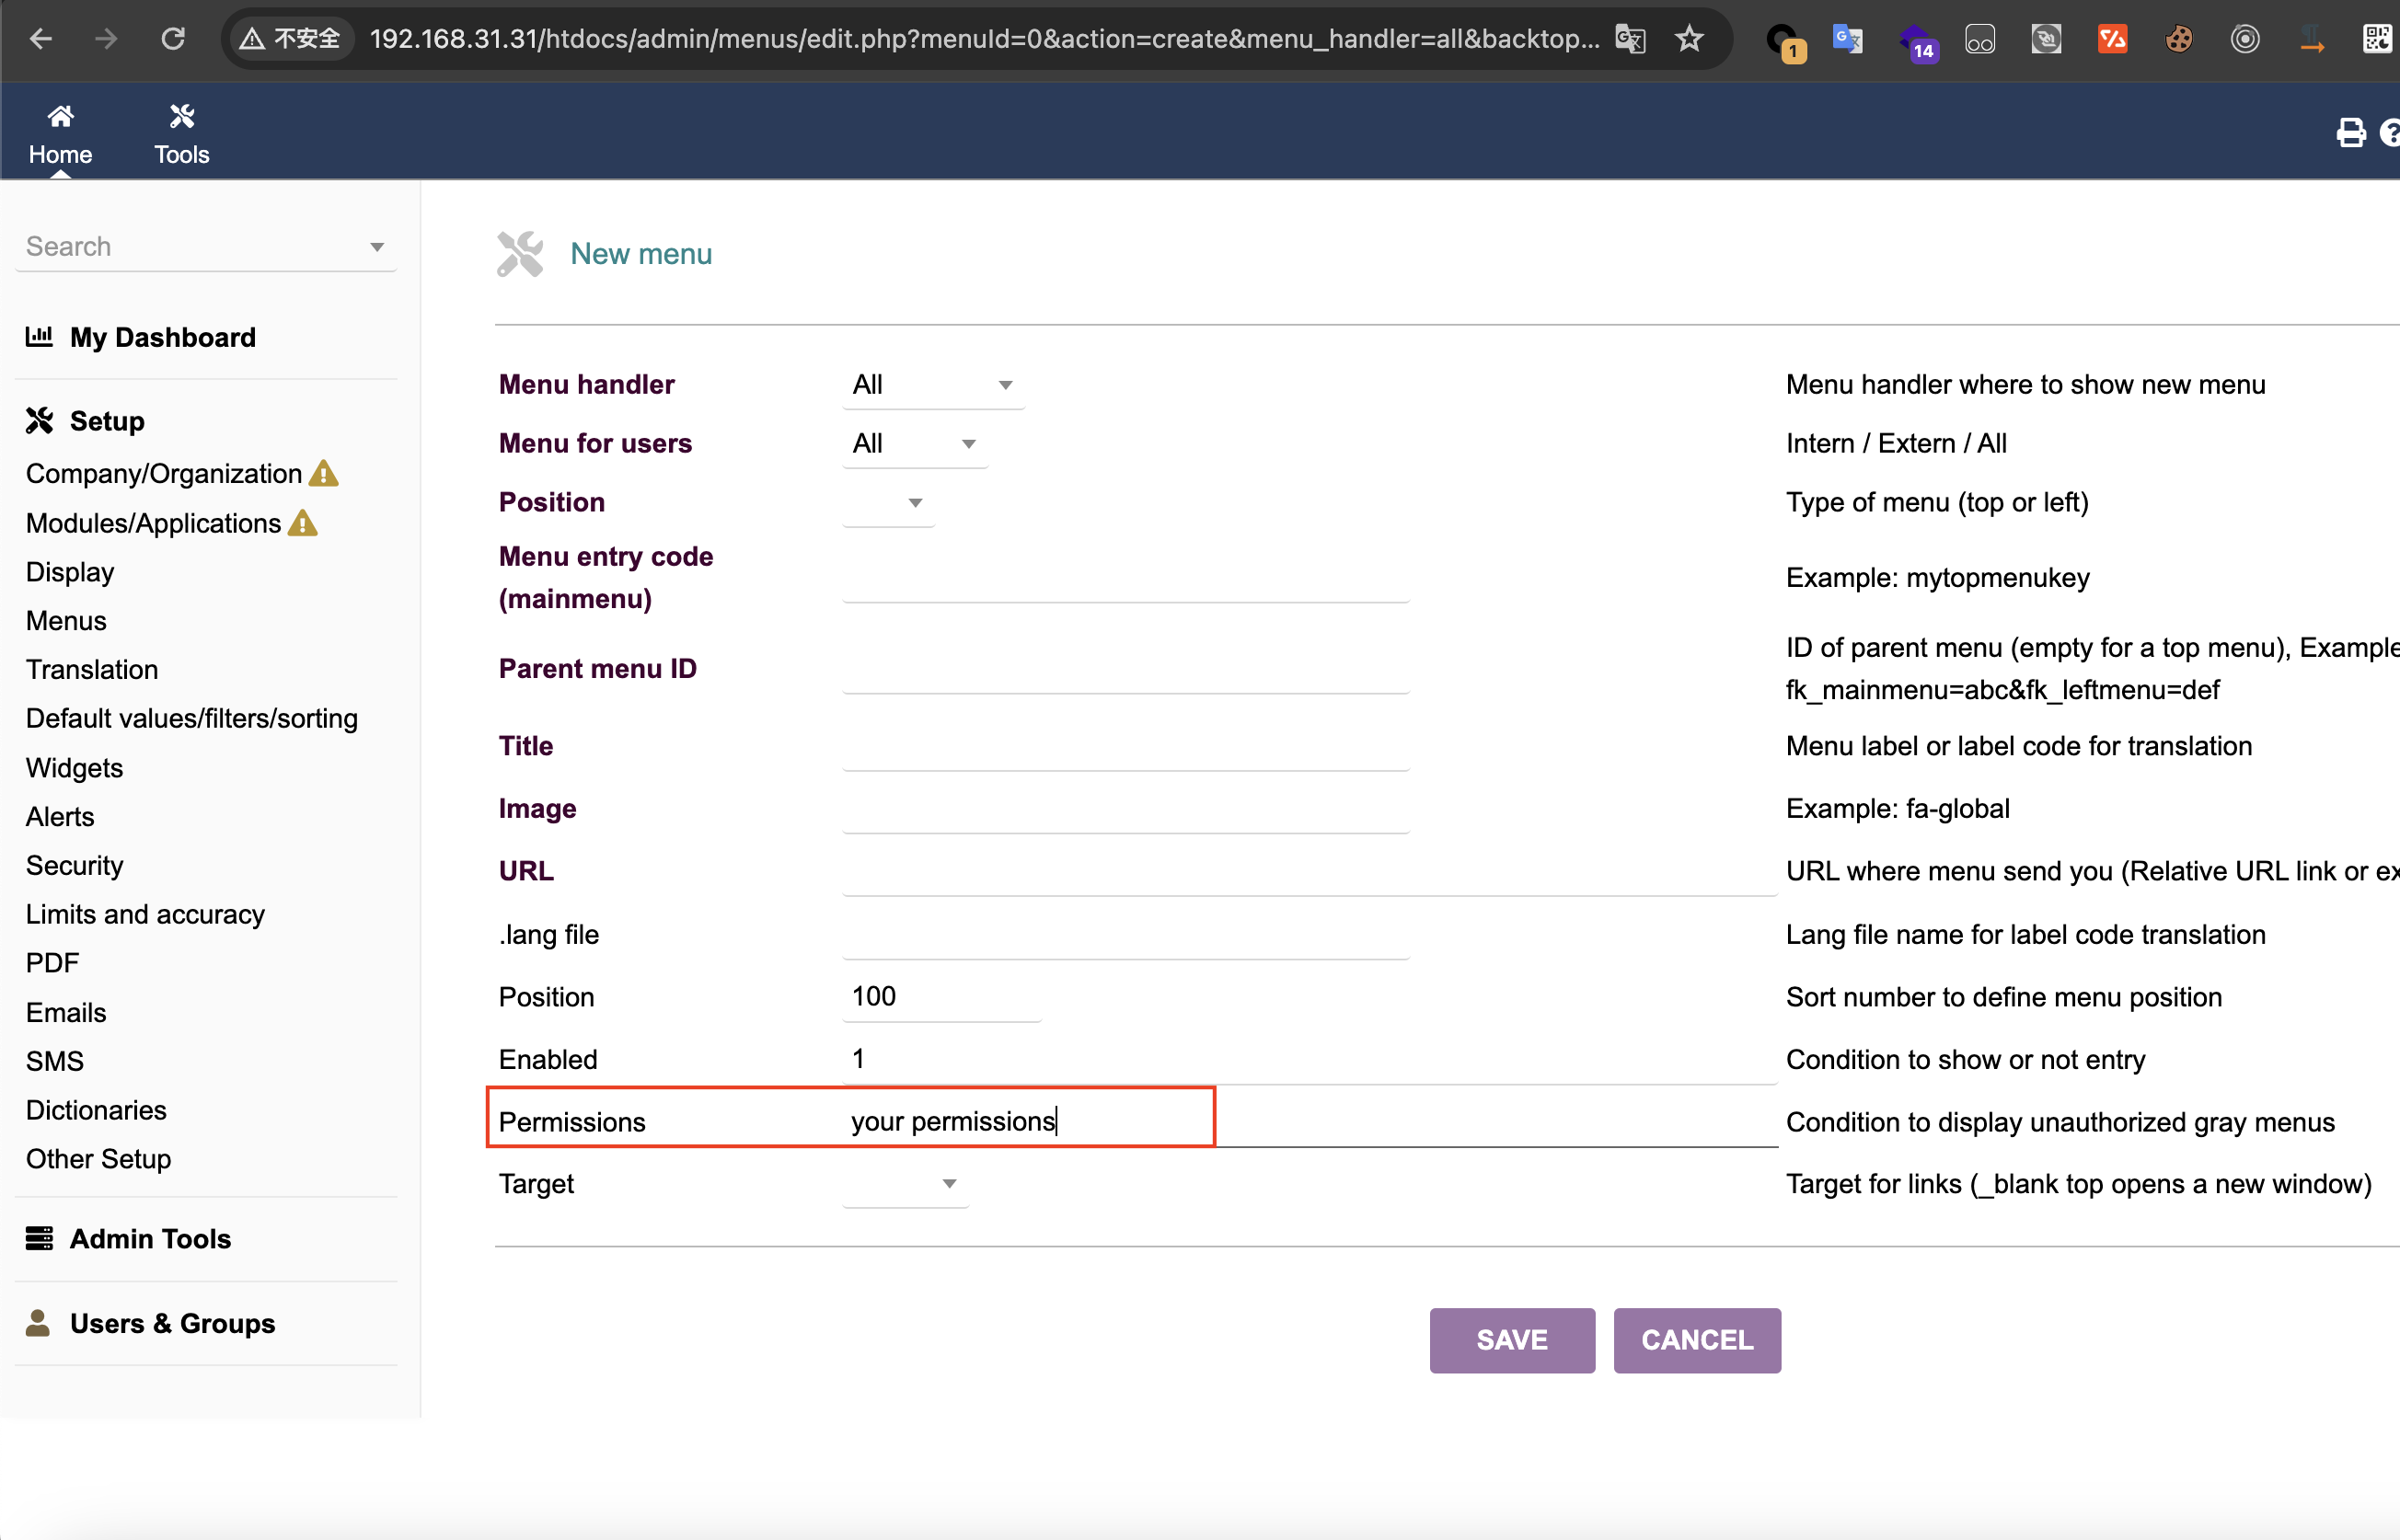 This is the trigger point of the vulnerabili…
-
High —
RageAgainstThePixel/setup-steamcmd leaked authentication token in job output logs
### Summary Log output includes authentication token that provides full account access ### Details The post job action prints the contents of `config/config.vdf` which holds the saved authentication token and can be used to sign in on another machine. This me…
-
High —
buildalon/setup-steamcmd leaked authentication token in job output logs
### Summary Log output includes authentication token that provides full account access ### Details The post job action prints the contents of `config/config.vdf` which holds the saved authentication token and can be used to sign in on another machine. This me…
-
Medium 6.3
fuyang_lipengjun platform SysLogController.java SysLogController sql injection
A vulnerability, which was classified as critical, was found in fuyang_lipengjun platform up to ca9aceff6902feb7b0b6bf510842aea88430796a. Affected is the function SysLogController of the file platform-admin/src/main/java/com/platform/controller/SysLogControll…
-
Medium 6.3
fuyang_lipengjun platform ScheduleJobController.java queryPage sql injection
A vulnerability, which was classified as critical, has been found in fuyang_lipengjun platform up to ca9aceff6902feb7b0b6bf510842aea88430796a. This issue affects the function queryPage of the file platform-schedule/src/main/java/com/platform/controller/Schedu…
-
Medium 5.2
IBM Cognos Analytics Mobile (iOS) authentication bypass
IBM Cognos Analytics Mobile (iOS) 1.1.0 through 1.1.22 is vulnerable to authentication bypass by using the Local Authentication Framework library which is not needed as biometric authentication is not used in the application.
-
Medium 5.9
IBM Cognos Analytics Mobile (iOS) information disclosure
IBM Cognos Analytics Mobile (iOS) 1.1.0 through 1.1.22 could be vulnerable to information exposure due to the use of unencrypted network traffic.
-
Medium 6.5
IBM Cognos Analytics Mobile (iOS) information disclosure
IBM Cognos Analytics Mobile (iOS) 1.1.0 through 1.1.22 could allow malicious actors to view and modify information coming to and from the application which could then be used to access confidential information on the device or network by using a the deprecate…
-
Medium 5.9
IBM Cognos Analytics Mobile (iOS) information disclosure
IBM Cognos Analytics Mobile (iOS) 1.1.0 through 1.1.22 could allow malicious actors to obtain sensitive information due to the cleartext transmission of data.
-
High 7.3
Campcodes Sales and Inventory System Setting settings_update.php sql injection
A vulnerability classified as critical was found in Campcodes Sales and Inventory System 1.0. This vulnerability affects unknown code of the file /pages/settings_update.php of the component Setting Handler. The manipulation of the argument ID leads to sql inj…
-
Medium 6.5
EspoCRM vulnerable to LDAP Injection through Improper Neutralization of Special Elements
EspoCRM is an Open Source CRM (Customer Relationship Management) software. EspoCRM versions 9.1.6 and earlier are vulnerable to blind LDAP Injection when LDAP authentication is enabled. A remote, unauthenticated attacker can manipulate LDAP queries by injecti…
-
Medium 6.0
Jakarta Mail vulnerable to SMTP Injection
In Jakarta Mail versions prior to 2.0.2 it is possible to perform an SMTP Injection by utilizing the \r and \n UTF-8 characters to separate different messages.
-
Medium 6.3
D-Link DIR‑817L ssdpcgi lxmldbc_system command injection
A vulnerability classified as critical has been found in D-Link DIR‑817L up to 1.04B01. This affects the function lxmldbc_system of the file ssdpcgi. The manipulation leads to command injection. It is possible to initiate the attack remotely. The exploit has …
-
High 7.5
File Download - Moderately critical - Access bypass - SA-CONTRIB-2025-089
Missing Authorization vulnerability in Drupal File Download allows Forceful Browsing.This issue affects File Download: from 0.0.0 before 1.9.0, from 2.0.0 before 2.0.1.
-
Medium 6.1
Real-time SEO for Drupal - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-091
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Real-time SEO for Drupal allows Cross-Site Scripting (XSS).This issue affects Real-time SEO for Drupal: from 2.0.0 before 2.2.0.
-
Medium 6.1
Block Attributes - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-090
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Block Attributes allows Cross-Site Scripting (XSS).This issue affects Block Attributes: from 0.0.0 before 1.1.0, from 2.0.0 before 2.0.1.
-
Medium 6.1
Cookies Addons - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-087
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Cookies Addons allows Cross-Site Scripting (XSS).This issue affects Cookies Addons: from 1.0.0 before 1.2.4.
-
Critical 9.8
Mail Login - Critical - Access bypass - SA-CONTRIB-2025-088
Improper Restriction of Excessive Authentication Attempts vulnerability in Drupal Mail Login allows Brute Force.This issue affects Mail Login: from 3.0.0 before 3.2.0, from 4.0.0 before 4.2.0.
-
Medium 4.4
Dell PowerScale OneFS, versions prior to 9.11.0.0, contains a use of a broken or risky cryptographic algorithm vulnerab…
-
High 7.3
code-projects Church Donation System admin_pic.php unrestricted upload
A vulnerability was found in code-projects Church Donation System 1.0. It has been rated as critical. Affected by this issue is some unknown functionality of the file /members/admin_pic.php. The manipulation of the argument image leads to unrestricted upload.…
-
Medium 6.6
Dell AppSync, version(s) 4.6.0.0, contains an Unrestricted Upload of File with Dangerous Type vulnerability. A high pri…
-
High 8.1
nova-tiptap has an Unauthenticated Arbitrary File Upload Vulnerability
marshmallow-packages/nova-tiptap is a rich text editor for Laravel Nova based on tiptap. Prior to 5.7.0, a vulnerability was discovered in the marshmallow-packages/nova-tiptap Laravel Nova package that allows unauthenticated users to upload arbitrary files to…
-
Medium 4.2
Dell AppSync, version(s) 4.6.0.0, contains an Improper Restriction of XML External Entity Reference vulnerability. A lo…
-
High 7.3
code-projects Church Donation System add_members.php sql injection
A vulnerability was found in code-projects Church Donation System 1.0. It has been declared as critical. Affected by this vulnerability is an unknown functionality of the file /members/add_members.php. The manipulation of the argument mobile leads to sql inje…
-
High 7.3
code-projects Church Donation System edit_Members.php sql injection
A vulnerability was found in code-projects Church Donation System 1.0. It has been classified as critical. Affected is an unknown function of the file /members/edit_Members.php. The manipulation of the argument fname leads to sql injection. It is possible to …
-
High 7.3
code-projects Church Donation System edit_user.php sql injection
A vulnerability was found in code-projects Church Donation System 1.0 and classified as critical. This issue affects some unknown processing of the file /members/edit_user.php. The manipulation of the argument firstname leads to sql injection. The attack may …
-
Medium 6.3
PHPGurukul Online Banquet Booking System view-user-queries.php sql injection
A vulnerability has been found in PHPGurukul Online Banquet Booking System 1.0 and classified as critical. This vulnerability affects unknown code of the file /admin/view-user-queries.php. The manipulation of the argument viewid leads to sql injection. The at…
-
High —
Alchemy Non-SMA and Webauthn Account Security Advisory
### Impact A potential security issue has been mitigated on old account deployment functions from the factory. Smart wallets in use on all existing supported networks are not impacted. ### Patches Please direct creation of new wallets to either `createSemiMod…
-
Medium 5.3
ExtremeControl (NAC) 'onmouseover' XSS
In ExtremeControl before 25.5.12, a cross-site scripting (XSS) vulnerability was discovered in a login interface of the affected application. The issue stems from improper handling of user-supplied input within HTML attributes, allowing an attacker to inject …
-
High 7.5
Hardcoded Credentials in PAVO Inc.'s PAVO Pay
Use of Hard-coded Credentials vulnerability in PAVO Inc. PAVO Pay allows Read Sensitive Constants Within an Executable. This issue affects PAVO Pay: before 13.05.2025.
-
High 7.5
IDOR in PAVO Inc.'s PAVO Pay
Authorization Bypass Through User-Controlled Key vulnerability in PAVO Inc. PAVO Pay allows Exploitation of Trusted Identifiers. This issue affects PAVO Pay: before 13.05.2025.
-
Medium 6.8CVE-2024-13973 EPSS 12%
A post-auth SQL injection vulnerability in WebAdmin of Sophos Firewall versions older than 21.0 MR1 (21.0.1) can potent…
-
High 8.1
A business logic vulnerability in the Up2Date component of Sophos Firewall older than version 21.0 MR1 (20.0.1) can lea…
-
Low 3.5
PHPGurukul Online Banquet Booking System booking-search.php cross site scripting
A vulnerability, which was classified as problematic, was found in PHPGurukul Online Banquet Booking System 1.0. This affects an unknown part of the file /admin/booking-search.php. The manipulation of the argument searchdata leads to cross site scripting. It …
-
High 8.8
A command injection vulnerability in WebAdmin of Sophos Firewall versions older than 21.0 MR2 (21.0.2) can lead to adja…
-
Critical 9.8CVE-2025-7624 EPSS 11%
An SQL injection vulnerability in the legacy (transparent) SMTP proxy of Sophos Firewall versions older than 21.0 MR2 (…
-
Critical 9.8CVE-2025-6704 EPSS 12%
An arbitrary file writing vulnerability in the Secure PDF eXchange (SPX) feature of Sophos Firewall versions older than…
-
High 7.5
A Recursor configured to send out ECS enabled queries can be sensitive to spoofing attempts
An attacker spoofing answers to ECS enabled requests sent out by the Recursor has a chance of success higher than non-ECS enabled queries. The updated version include various mitigations against spoofing attempts of ECS enabled queries by chaining ECS enabled…
-
Medium 5.9
Incorrect authentication in ParkingDoor
Incorrect authentication vulnerability in ParkingDoor. Through this vulnerability it is possible to operate the device without the access being logged in the application and even if the access permissions have been revoked.