
40 results · Clear filters · Feed
-
High 8.8
Dolibarr: SQL Injection in societe/class/societe.class.php via localtax1_value parameter
Dolibarr is an open-source enterprise resource planning and customer relationship management application. Prior to 22.0.5 and 23.0.1, there is a SQL injection vulnerability in the Third Party company update functionality. The application concatenates the loc…
-
High 8.8
Dolibarr Allows Code Injection through its Website Module
In Dolibarr ERP & CRM <= 22.0.4, PHP code detection and editing permission enforcement in the Website module is not applied consistently to all input parameters, allowing an authenticated user restricted to HTML/JavaScript editing to inject PHP code through u…
-
High 8.8
Dolibarr user with permission to edit PHP content can bypass filtering to restrict dangerous PHP functions
In the Website module of Dolibarr ERP & CRM 22.0.4 and below, the application uses blacklist-based filtering to restrict dangerous PHP functions related to system command execution. An authenticated user with permission to edit PHP content can bypass this fil…
-
High 8.2
Dolibarr ERP-CRM 8.0.4 SQL Injection via rowid Parameter
Dolibarr ERP-CRM 8.0.4 contains an SQL injection vulnerability in the rowid parameter of the admin dict.php endpoint that allows attackers to execute arbitrary SQL queries. Attackers can inject malicious SQL code through the rowid POST parameter to extract se…
-
High 8.8
Dolibarr vulnerable to RCE via the computed field parameter
Dolibarr ERP & CRM v21.0.1 were discovered to contain a remote code execution (RCE) vulnerability in the User module configuration via the computed field parameter.
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 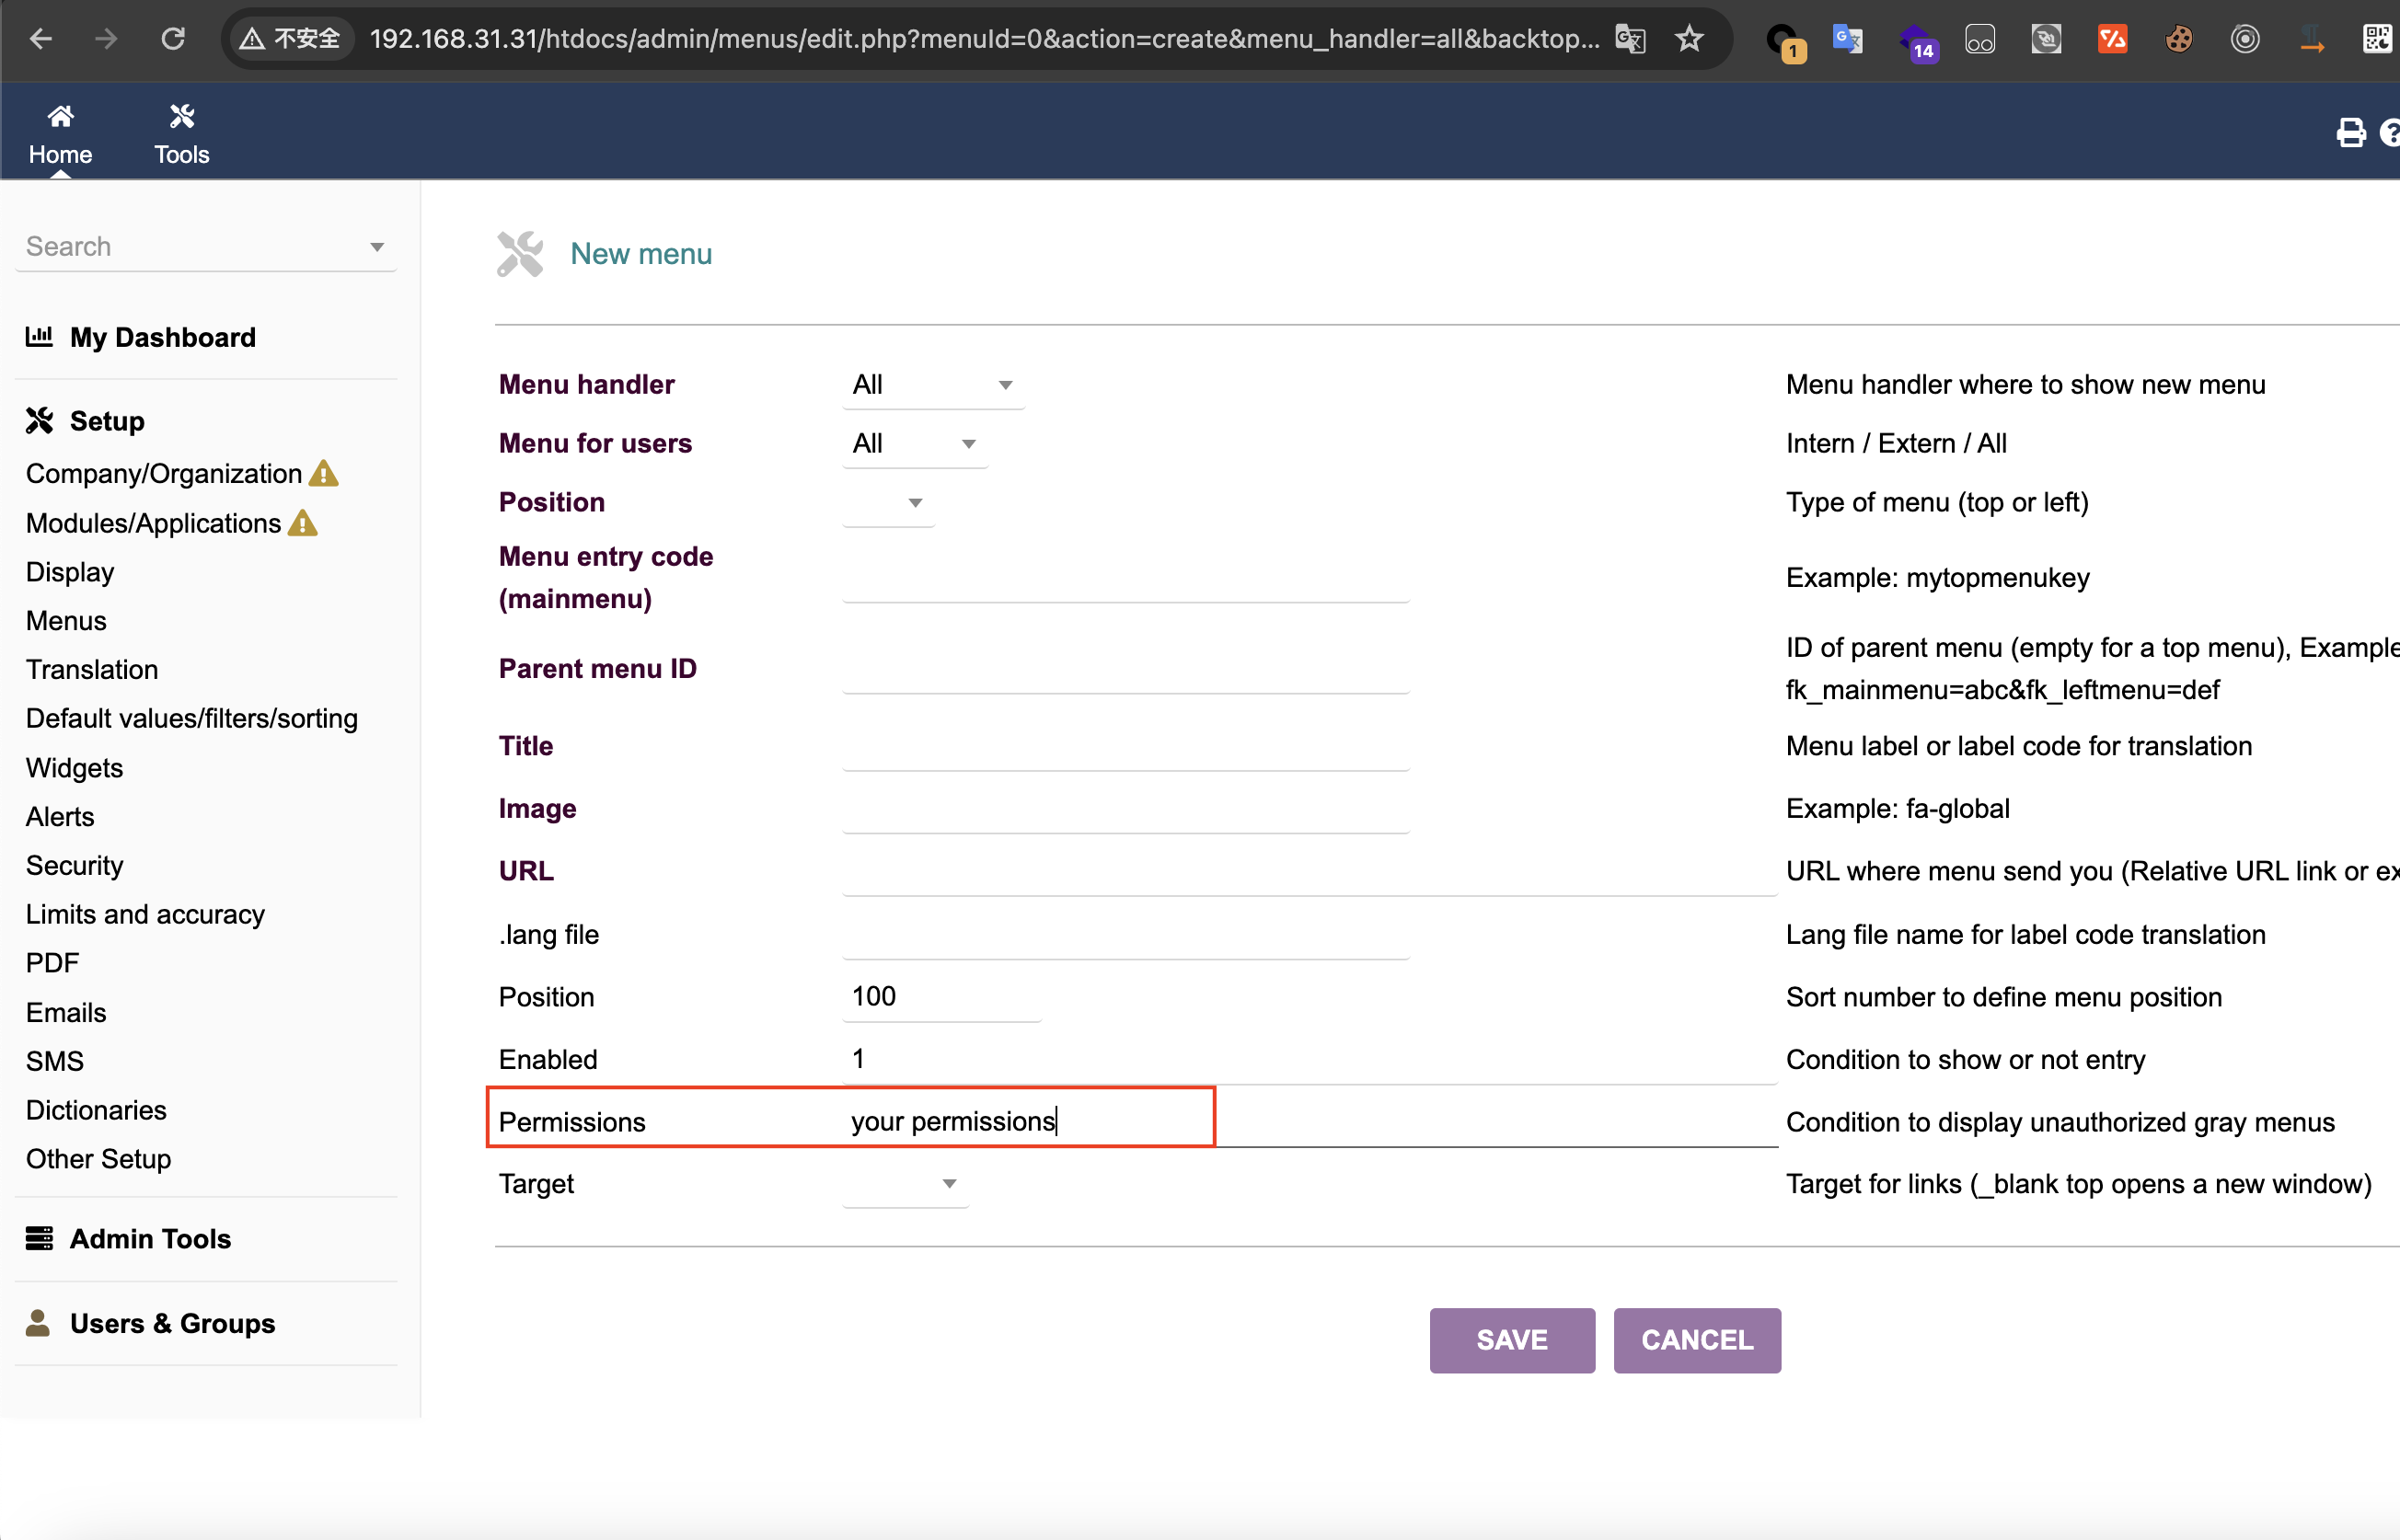 This is the trigger point of the vulnerabili…
-
High 8.8
Dolibarr arbitrary file upload vulnerability
An arbitrary file upload vulnerability in the Upload Template function of Dolibarr ERP CRM up to v19.0.1 allows attackers to execute arbitrary code via uploading a crafted .SQL file.
-
High 7.5
Dolibarr vulnerable to Cross-Site Request Forgery
Incorrect access control in Dolibarr ERP CRM versions 19.0.0 and before, allows authenticated attackers to steal victim users' session cookies and CSRF protection tokens via user interaction with a crafted web page, leading to account takeover.
-
High 8.8
Dolibarr ERP CRM Code Injection vulnerability during installation
Lack of sanitization during Installation Process in Dolibarr ERP CRM up to version 19.0.0 allows an attacker with adjacent access to the network to execute arbitrary code via a specifically crafted input.
-
High 7.1
Dolibarr Application Home Page HTML injection vulnerability
Dolibarr is an enterprise resource planning (ERP) and customer relationship management (CRM) software package. Version 18.0.4 has a HTML Injection vulnerability in the Home page of the Dolibarr Application. This vulnerability allows an attacker to inject arbi…
-
High 7.5
Dolibarr ERP CRM (<= 18.0.1) Improper Input Sanitization Authenticated RCE
Improper input validation in Dolibarr ERP CRM <= v18.0.1 fails to strip certain PHP code from user-supplied input when creating a Website, allowing an attacker to inject and evaluate arbitrary PHP code.
-
High 8.8
File Upload vulnerability in Dolibarr ERP CRM
File Upload vulnerability in Dolibarr ERP CRM v.17.0.1 and before allows a remote attacker to execute arbitrary code and obtain sensitive information via the extension filtering and renaming functions.
-
High 7.2CVE-2023-38886 EPSS 30%
Dolibarr allows a remote privileged attacker to execute arbitrary code via a crafted command/script
An issue in Dolibarr ERP CRM v.17.0.1 and before allows a remote privileged attacker to execute arbitrary code via a crafted command/script.
-
High 7.5
Dolibarr vulnerable to unauthenticated database access
An issue in Dolibarr 16 before 16.0.5 allows unauthenticated attackers to perform a database dump and access a company's entire customer file, prospects, suppliers, and employee information if a contact file exists.
-
High 8.8
Dolibarr vulnerable to remote code execution via uppercase manipulation
Dolibarr before 17.0.1 allows remote code execution by an authenticated user via an uppercase manipulation: <?PHP instead of <?php in injected data.
-
High 8.1
SQL Injection in dolibarr/dolibarr
SQL injection attacks can result in unauthorized access to sensitive data, such as passwords, credit card details, or personal user information. Many high-profile data breaches in recent years have been the result of SQL injection attacks, leading to reputati…
-
High 8.4
Cross-site Scripting (XSS) - Stored in dolibarr/dolibarr
Cross-site Scripting (XSS) - Stored in GitHub repository dolibarr/dolibarr prior to 16.0.
-
High 7.5
Access Control vulnerability in Dolibarr
An Access Control vulnerability exists in Dolibarr ERP/CRM 13.0.2, fixed version is 14.0.0,in the forgot-password function becuase the application allows email addresses as usernames, which can cause a Denial of Service.
-
High 8.8
SQL Injection in Dolibarr
An SQL Injection vulnerability exists in Dolibarr ERP/CRM 13.0.2 (fixed version is 14.0.0) via a POST request to the country_id parameter in an UPDATE statement.
-
High 7.2CVE-2022-0819 EPSS 43%
Code Injection in dolibarr/dolibarr
Code Injection in GitHub repository dolibarr/dolibarr prior to 15.0.1.
-
High 8.3
SQL Injection in dolibarr/dolibarr
dolibarr is vulnerable to Improper Neutralization of Special Elements used in an SQL Command
-
High 8.8
Account Takeover in "Dolibarr" via Password Reset Functionality
In “Dolibarr” application, v2.8.1 to v13.0.2 are vulnerable to account takeover via password reset functionality. A low privileged attacker can reset the password of any user in the application using the password reset link the user received through email whe…
-
High 7.2
Dolibarr authenticated Remote Code Execution
Dolibarr 12.0.3 is vulnerable to authenticated Remote Code Execution. An attacker who has the access the admin dashboard can manipulate the backup function by inserting a payload into the filename for the zipfilename_template parameter to admin/tools/dolibarr…
-
High 8.8
Dolibarr Unrestricted Upload of File with Dangerous Type
Dolibarr before 11.0.5 allows low-privilege users to upload files of dangerous types, leading to arbitrary code execution. This occurs because .pht and .phar files can be uploaded. Also, a .htaccess file can be uploaded to reconfigure access control (e.g., to…
-
High 8.8
Dolibarr SQL injection vulnerability in accountancy/customer/card.php
A SQL injection vulnerability in accountancy/customer/card.php in Dolibarr 11.0.3 allows remote authenticated users to execute arbitrary SQL commands via the id parameter.
-
High 8.8
Incorrect Authorization in Dolibarr
core/get_menudiv.php in Dolibarr before 11.0.4 allows remote authenticated attackers to bypass intended access restrictions via a non-alphanumeric menu parameter.
-
High 8.8
Dolibarr Cross-Site Request Forgery Vulnerability
In Dolibarr 10.0.6, forms are protected with a CSRF token against CSRF attacks. The problem is any CSRF token in any user's session can be used in another user's session. CSRF tokens should not be valid in this situation.
-
High 7.5
Dolibarr ERP and CRM SQLi
Dolibarr ERP/CRM before 10.0.3 allows SQL Injection.
-
High 8.0
Dolibarr Cross-Site Request Forgery (CSRF)
An issue was discovered in Dolibarr 11.0.0-alpha. A user can store an IFRAME element (containing a user/card.php CSRF request) in his Linked Files settings page. When visited by the admin, this could completely take over the admin account. (The protection mec…
-
High 8.0
Dolibarr ERP and CRM Code Injection
Dolibarr ERP/CRM 9.0.1 provides a module named website that provides for creation of public websites with a WYSIWYG editor. It was identified that the editor also allowed inclusion of dynamic code, which can lead to code execution on the host machine. An atta…
-
High 8.8
Dolibarr ERP and CRM malicious executable loading
Dolibarr ERP/CRM 9.0.1 provides a web-based functionality that backs up the database content to a dump file. However, the application performs insufficient checks on the export parameters to mysqldump, which can lead to execution of arbitrary binaries on the …
-
High 8.8CVE-2019-1010054 Public exploit
Dolibarr Cross Site Request Forgery (CSRF)
Dolibarr 7.0.0 is affected by: Cross Site Request Forgery (CSRF). The impact is: allow malitious html to change user password, disable users and disable password encryptation. The component is: Function User password change, user disable and password encrypta…
-
High 8.8
Dolibarr SQL injection vulnerability in user/card.php
SQL injection vulnerability in user/card.php in Dolibarr version 8.0.2 allows remote authenticated users to execute arbitrary SQL commands via the employee parameter.
-
High 8.8
Dolibarr error-based SQL injection vulnerability in product/card.php
An error-based SQL injection vulnerability in product/card.php in Dolibarr version 8.0.2 allows remote authenticated users to execute arbitrary SQL commands via the desiredstock parameter.
-
High 8.0
Dolibarr arbitrary commands execution
The admin panel in Dolibarr before 7.0.2 might allow remote attackers to execute arbitrary commands by leveraging support for updating the antivirus command and parameters used to scan file uploads.
-
High 8.8
Dolibarr SQL injection vulnerability
Dolibarr ERP/CRM is affected by multiple SQL injection vulnerabilities in versions through 7.0.0 via comm/propal/list.php (viewstatut parameter) or comm/propal/list.php (propal_statut parameter, aka search_statut parameter).
-
High 8.8
Dolibarr SQL injection via type parameter in product/stats/card.php
Dolibarr ERP/CRM is affected by SQL injection in versions before 5.0.4 via product/stats/card.php (type parameter).
-
High 7.5
Dolibarr sensitive information disclosure
Dolibarr ERP/CRM version 6.0.4 does not block direct requests to *.tpl.php files, which allows remote attackers to obtain sensitive information.
-
High 7.5
Dolibarr ERP and CRM Sensitive Data Disclosure
There is a sensitive information disclosure vulnerability in document.php in Dolibarr ERP/CRM version 6.0.0 via the file parameter.
-
High 8.8
Dolibarr ERP and CRM Unsafe File Upload Vulnerability
Dolibarr ERP/CRM 5.0.3 and prior allows low-privilege users to upload files of dangerous types, which can result in arbitrary code execution within the context of the vulnerable application.