
Ecosystem
Packagist
7,192 known vulnerabilities.
Most affected packages
1,968 results · Clear filters · Feed
-
High 7.6
Microweber Has Stored XSS Vulnerability in User Profile Fields
A Stored Cross-Site Scripting (XSS) vulnerability in Microweber CMS 2.0 allows attackers to inject malicious scripts into user profile fields, leading to arbitrary JavaScript execution in admin browsers.
-
High 8.1CVE-2025-45346 Public exploit
Bacula-web SQL Injection Vulnerability
SQL Injection vulnerability in Bacula-web before v.9.7.1 allows a remote attacker to execute arbitrary code via a crafted HTTP GET request.
-
High 8.3
HAX CMS Backend Lacks Comprehensive Authorization Checks
HAX CMS allows you to manage your microsite universe with PHP or NodeJs backends. In versions 11.0.13 and below of haxcms-nodejs and versions 11.0.8 and below of haxcms-php, API endpoints do not perform authorization checks when interacting with a resource. B…
-
High 7.5
LibreNMS has Authenticated Local File Inclusion in ajax_form.php that Allows RCE
LibreNMS is an auto-discovering PHP/MySQL/SNMP based network monitoring which includes support for a wide range of network hardware and operating systems. LibreNMS versions 25.6.0 and below contain an architectural vulnerability in the ajax_form.php endpoint …
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 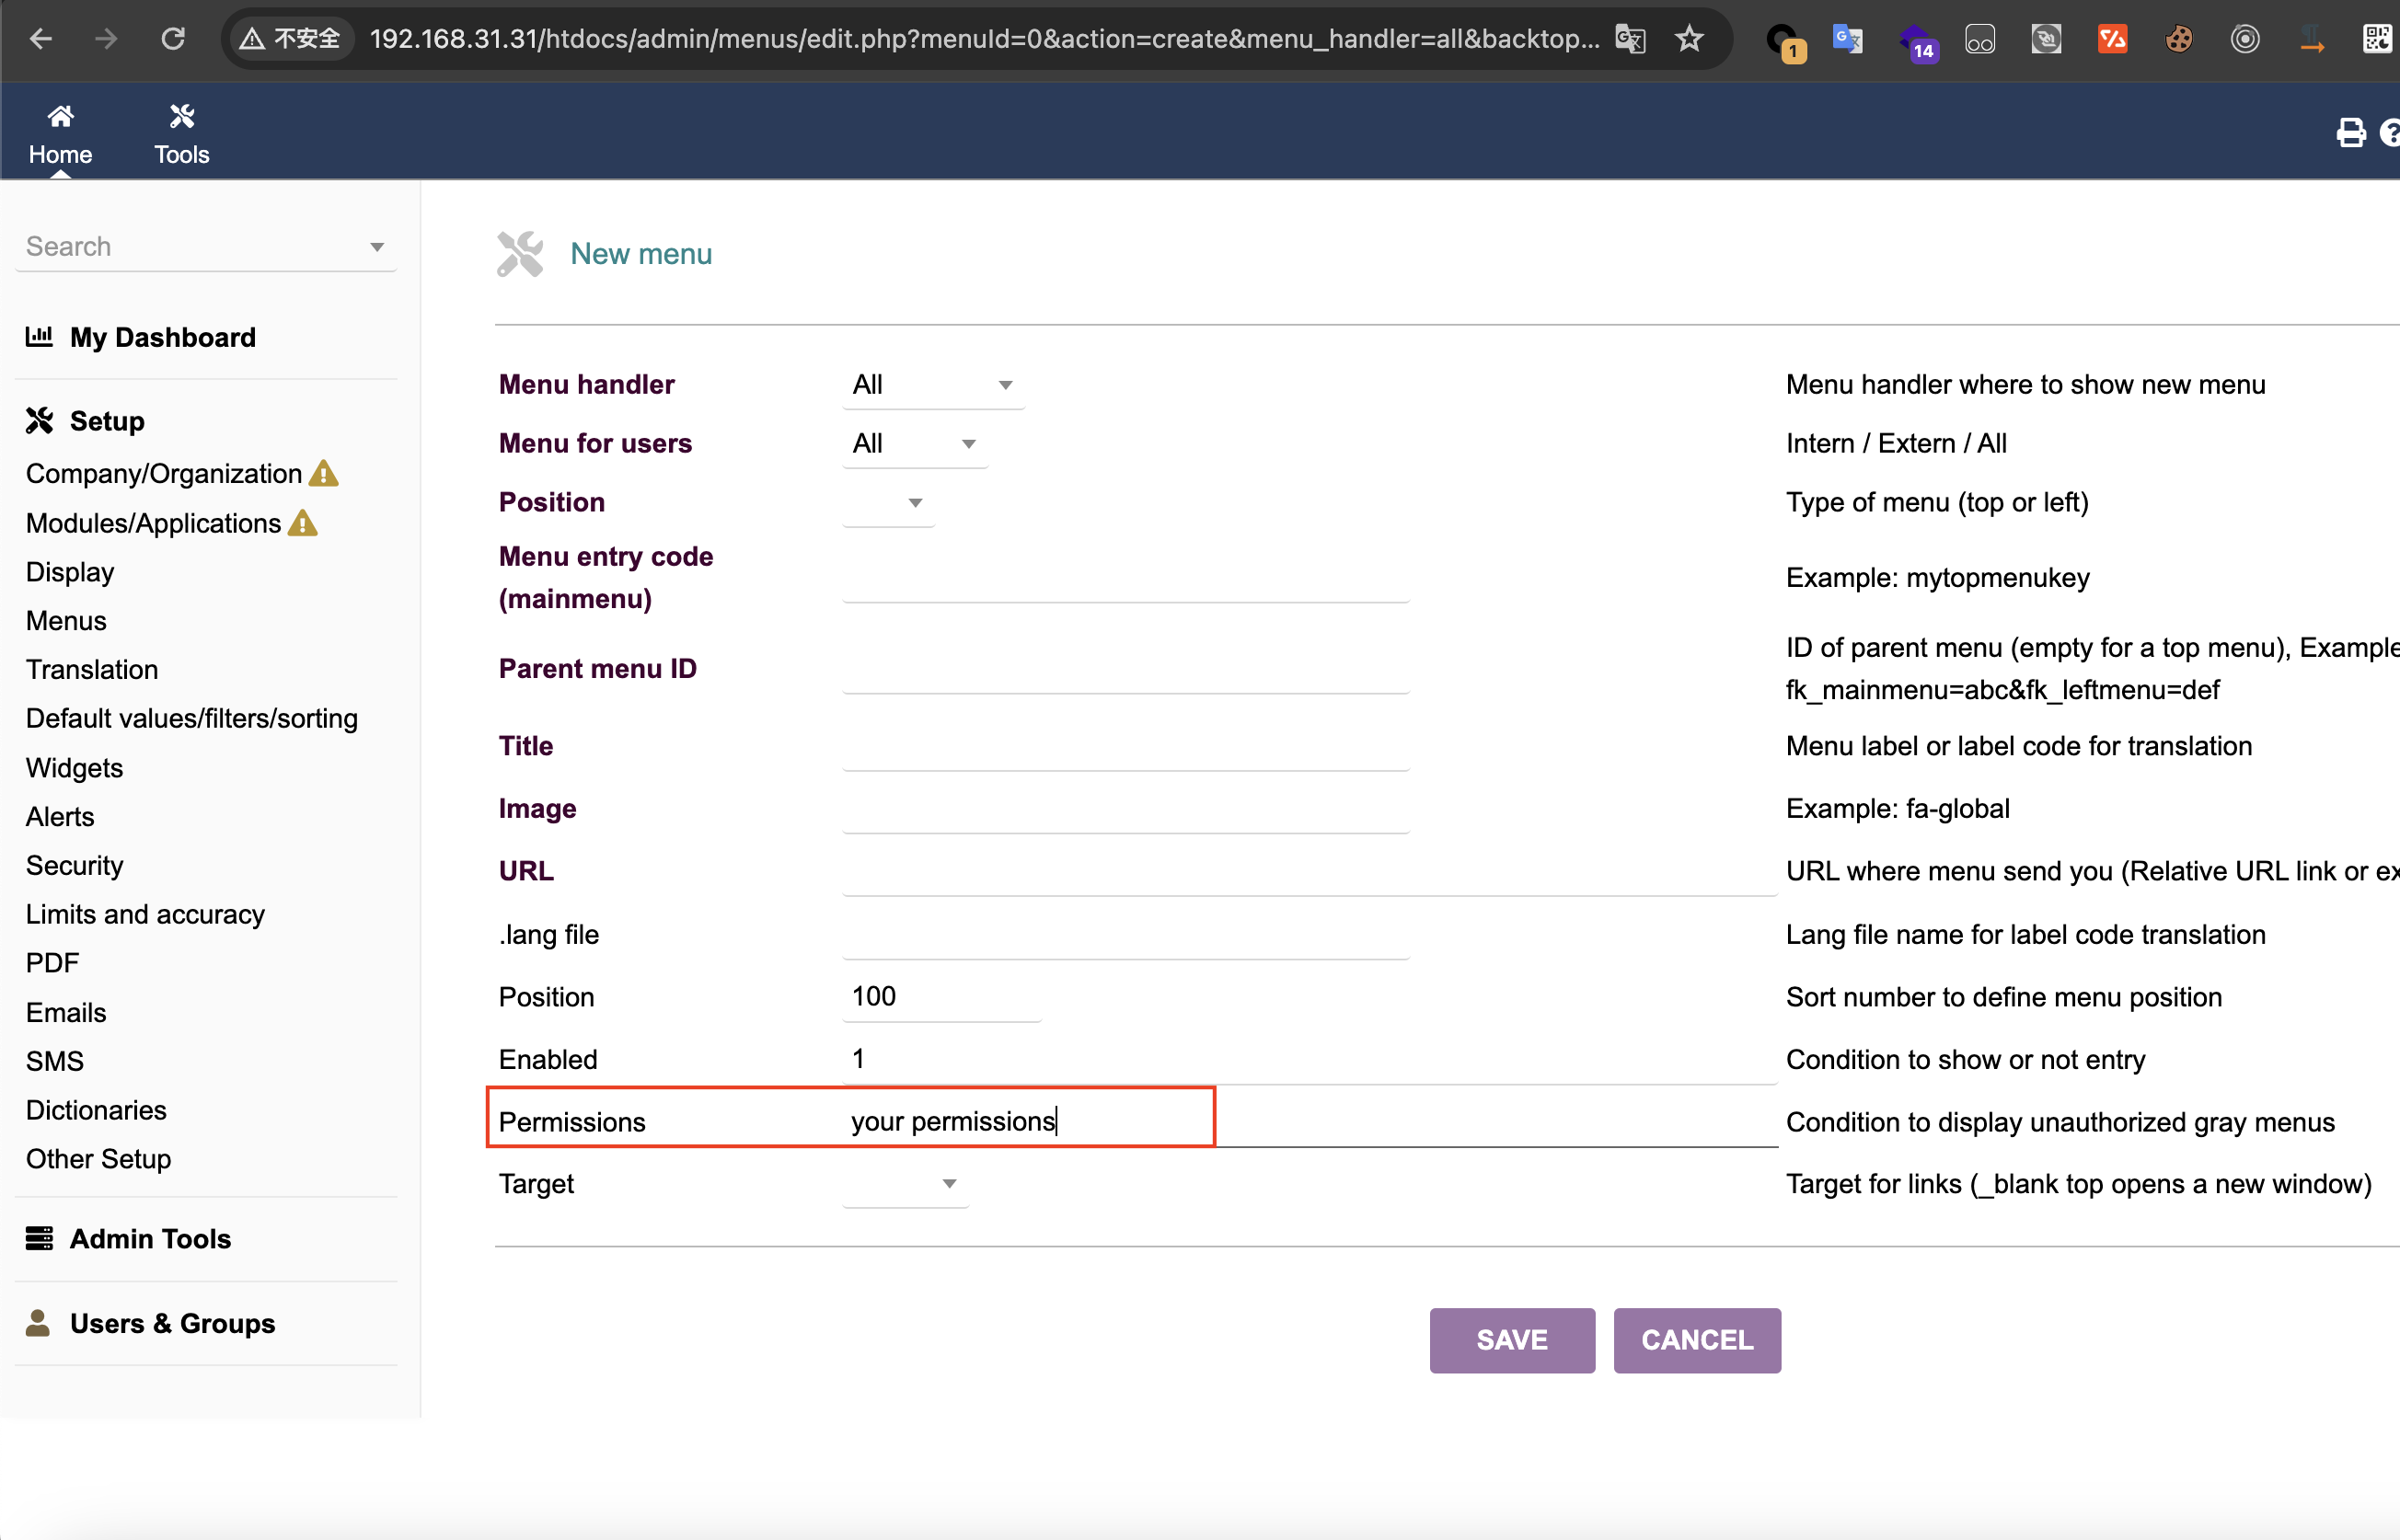 This is the trigger point of the vulnerabili…
-
High 7.5
File Download - Moderately critical - Access bypass - SA-CONTRIB-2025-089
Missing Authorization vulnerability in Drupal File Download allows Forceful Browsing.This issue affects File Download: from 0.0.0 before 1.9.0, from 2.0.0 before 2.0.1.
-
High 8.1
nova-tiptap has an Unauthenticated Arbitrary File Upload Vulnerability
marshmallow-packages/nova-tiptap is a rich text editor for Laravel Nova based on tiptap. Prior to 5.7.0, a vulnerability was discovered in the marshmallow-packages/nova-tiptap Laravel Nova package that allows unauthenticated users to upload arbitrary files to…
-
High 8.7
DynamicPageList3 exposes hidden/suppressed usernames
The DynamicPageList3 extension is a reporting tool for MediaWiki, listing category members and intersections with various formats and details. Several #dpl parameters can leak usernames that have been hidden using revision deletion, suppression, or the hideus…
-
High 8.6
Citizen Short Description stored XSS vulnerability through wikitext
Short Description is a MediaWiki extension that provides local short description support. In version 4.0.0, short descriptions are not properly sanitized before being inserted as HTML using mw.util.addSubtitle, allowing any user to insert arbitrary HTML into …
-
High 7.5CVE-2025-34086 Public exploit
Bolt CMS Authenticated Remote Code Execution via Profile Injection and File Rename
Bolt CMS versions 3.7.0 and earlier contain a chain of vulnerabilities that together allow an authenticated user to achieve remote code execution. A user with valid credentials can inject arbitrary PHP code into the displayname field of the user profile, whic…
-
High 8.6
Citizen stored XSS vulnerability through short descriptions
Citizen is a MediaWiki skin that makes extensions part of the cohesive experience. From versions 1.9.4 to before 3.4.0, short descriptions set via the ShortDescription extension are inserted as raw HTML by the Citizen skin, allowing any user to insert arbitra…
-
High 8.6
Citizen is vulnerable to stored XSS attack in the legacy search bar
Citizen is a MediaWiki skin that makes extensions part of the cohesive experience. From versions 1.9.4 to before 3.4.0, page descriptions are inserted into raw HTML without proper sanitization by the Citizen skin when using the old search bar. Any user with p…
-
High 8.6
TabberNeue vulnerable to Stored XSS through wikitext
TabberNeue is a MediaWiki extension that allows the wiki to create tabs. Starting in version 3.0.0 and prior to version 3.1.1, any user can insert arbitrary HTMLinto the DOM by inserting a payload into any allowed attribute of the `<tabber>` tag. Version 3.1.…
-
High 8.6
COOKiES Consent Management - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-076
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal COOKiES Consent Management allows Cross-Site Scripting (XSS).This issue affects COOKiES Consent Management: from 0.0.0 before 1.2.15.
-
High 8.6
COOKiES Consent Management - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-075
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal COOKiES Consent Management allows Cross-Site Scripting (XSS).This issue affects COOKiES Consent Management: from 0.0.0 before 1.2.15.
-
High 7.3
etracker - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-074
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal etracker allows Cross-Site Scripting (XSS).This issue affects etracker: from 0.0.0 before 3.1.0.
-
High 8.8
Simple Klaro - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-071
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Simple Klaro allows Cross-Site Scripting (XSS).This issue affects Simple Klaro: from 0.0.0 before 1.10.0.
-
High 7.1
Lightgallery - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-069
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Lightgallery allows Cross-Site Scripting (XSS).This issue affects Lightgallery: from 0.0.0 before 1.6.0.
-
High 8.8
Commerce Alphabank Redirect - Moderately critical - Access bypass - SA-CONTRIB-2025-067
Incorrect Authorization vulnerability in Drupal Commerce Alphabank Redirect allows Functionality Misuse.This issue affects Commerce Alphabank Redirect: from 0.0.0 before 1.0.3.
-
High 8.8
Commerce Eurobank (Redirect) - Moderately critical - Access bypass - SA-CONTRIB-2025-066
Incorrect Authorization vulnerability in Drupal Commerce Eurobank (Redirect) allows Functionality Misuse.This issue affects Commerce Eurobank (Redirect): from 0.0.0 before 2.1.1.
-
High 8.4
Adobe Commerce | Cross-site Scripting (Stored XSS) (CWE-79)
Adobe Commerce versions 2.4.8, 2.4.7-p5, 2.4.6-p10, 2.4.5-p12, 2.4.4-p13 and earlier are affected by a stored Cross-Site Scripting (XSS) vulnerability that could be abused by a high-privileged attacker to inject malicious scripts into vulnerable form fields. …
-
High 8.2
Adobe Commerce | Improper Authorization (CWE-285)
Adobe Commerce versions 2.4.8, 2.4.7-p5, 2.4.6-p10, 2.4.5-p12, 2.4.4-p13 and earlier are affected by an Improper Authorization vulnerability that could result in a Security feature bypass. An attacker could leverage this vulnerability to bypass security measu…
-
High 8.5
Hax CMS Stored Cross-Site Scripting vulnerability
HAX CMS PHP allows users to manage their microsite universe with a PHP backend. Prior to version 11.0.0, the application does not sufficiently sanitize user input, allowing for the execution of arbitrary JavaScript code. The 'saveNode' and 'saveManifest' endp…
-
High 8.7
PHPOffice Math allows XXE when processing an XML file in the MathML format
PHPOffice Math is a library that provides a set of classes to manipulate different formula file formats. Prior to version 0.3.0, loading XML data using the standard `libxml` extension and the `LIBXML_DTDLOAD` flag without additional filtration, leads to XXE. …
-
High 7.5
Events Log Track - Moderately critical - Denial of Service - SA-CONTRIB-2025-059
Allocation of Resources Without Limits or Throttling vulnerability in Drupal Events Log Track allows Excessive Allocation.This issue affects Events Log Track: from 0.0.0 before 3.1.11, from 4.0.0 before 4.0.2.
-
High 8.6
The Front End User Registration extension for TYPO3 (sr_feuser_register) allows Insecure Direct Object Reference
The sr_feuser_register extension through 12.4.8 for TYPO3 allows Insecure Direct Object Reference.
-
High 8.6
reint_downloadmanager TYPO3 Extension is susceptible to Insecure Direct Object Reference
The reint_downloadmanager extension through 5.0.0 for TYPO3 allows Insecure Direct Object Reference.
-
High 8.6
The Backup Plus extension for TYPO3 (ns_backup) has a Predictable Resource Location
The ns_backup extension through 13.0.0 for TYPO3 has a Predictable Resource Location.
-
High 7.2
TYPO3 Has Broken Authentication in Backend MFA
TYPO3 is an open source, PHP based web content management system. In versions on the 12.x branch prior to 12.4.31 LTS and the 13.x branch prior to 13.4.2 LTS, the multifactor authentication (MFA) dialog presented during backend login can be bypassed due to in…
-
High 7.2
TYPO3 CMS Vulnerable to Privilege Escalation to System Maintainer
TYPO3 is an open source, PHP based web content management system. Starting in version 10.0.0 and prior to versions 10.4.50 ELTS, 11.5.44 ELTS, 12.4.31 LTS, and 13.4.12 LTS, administrator-level backend users without system maintainer privileges can escalate th…
-
High 7.4
Enterprise MFA - TFA for Drupal - Critical - Access bypass - SA-CONTRIB-2025-056
Authentication Bypass Using an Alternate Path or Channel vulnerability in Drupal Enterprise MFA - TFA for Drupal allows Authentication Bypass.This issue affects Enterprise MFA - TFA for Drupal: from 0.0.0 before 4.7.0, from 5.0.0 before 5.2.0.
-
High 8.8
Enterprise MFA - TFA for Drupal - Critical - Cross Site Request Forgery - SA-CONTRIB-2025-054
Cross-Site Request Forgery (CSRF) vulnerability in Drupal Enterprise MFA - TFA for Drupal allows Cross Site Request Forgery.This issue affects Enterprise MFA - TFA for Drupal: from 0.0.0 before 4.7.0, from 5.0.0 before 5.2.0.
-
High 7.5
Enterprise MFA - TFA for Drupal - Moderately critical - Access bypass - SA-CONTRIB-2025-053
Authentication Bypass Using an Alternate Path or Channel vulnerability in Drupal Enterprise MFA - TFA for Drupal allows Authentication Bypass.This issue affects Enterprise MFA - TFA for Drupal: from 0.0.0 before 4.7.0, from 5.0.0 before 5.2.0.
-
High 8.8
Restrict route by IP - Critical - Cross Site Request Forgery - SA-CONTRIB-2025-047
Cross-Site Request Forgery (CSRF) vulnerability in Drupal Restrict route by IP allows Cross Site Request Forgery.This issue affects Restrict route by IP: from 0.0.0 before 1.3.0.
-
High 7.5
OXID eShop May Display User Information
An issue was discovered in OXID eShop before 7. CMS pages in combination with Smarty may display user information if a CMS page contains a Smarty syntax error.
-
High 7.5CVE-2025-29448 Public exploit
Easy!Appointments Denial of Service (DoS)
Booking logic flaw in Easy!Appointments v1.5.1 allows unauthenticated attackers to create appointments with excessively long durations, causing a denial of service by blocking all future booking availability.
-
High 7.3CVE-2025-46731 Public exploit
Craft CMS Contains a Potential Remote Code Execution Vulnerability via Twig SSTI
Craft is a content management system. Versions of Craft CMS on the 4.x branch prior to 4.14.13 and on the 5.x branch prior to 5.6.16 contains a potential remote code execution vulnerability via Twig SSTI. One must have administrator access and `ALLOW_ADMIN_CH…
-
High 7.6CVE-2025-46349 Scanner template
YesWiki Vulnerable to Unauthenticated Reflected Cross-site Scripting
YesWiki is a wiki system written in PHP. Prior to version 4.5.4, YesWiki is vulnerable to reflected XSS in the file upload form. This vulnerability allows any malicious unauthenticated user to create a link that can be clicked on by the victim to perform arbi…
-
High 7.5CVE-2025-32044 Public exploit
Moodle: unauthenticated rest api user data exposure
A flaw has been identified in Moodle where, on certain sites, unauthenticated users could retrieve sensitive user data—including names, contact information, and hashed passwords—via stack traces returned by specific API calls. Sites with PHP configured with z…
-
High 8.8
Moodle: authenticated remote code execution risk in the moodle lms equella repository
A flaw was found in Moodle. A remote code execution risk was identified in the Moodle LMS EQUELLA repository. By default, this was only available to teachers and managers on sites with the EQUELLA repository enabled.