
Ecosystem
Packagist
7,191 known vulnerabilities.
Most affected packages
7,181 results · Feed
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 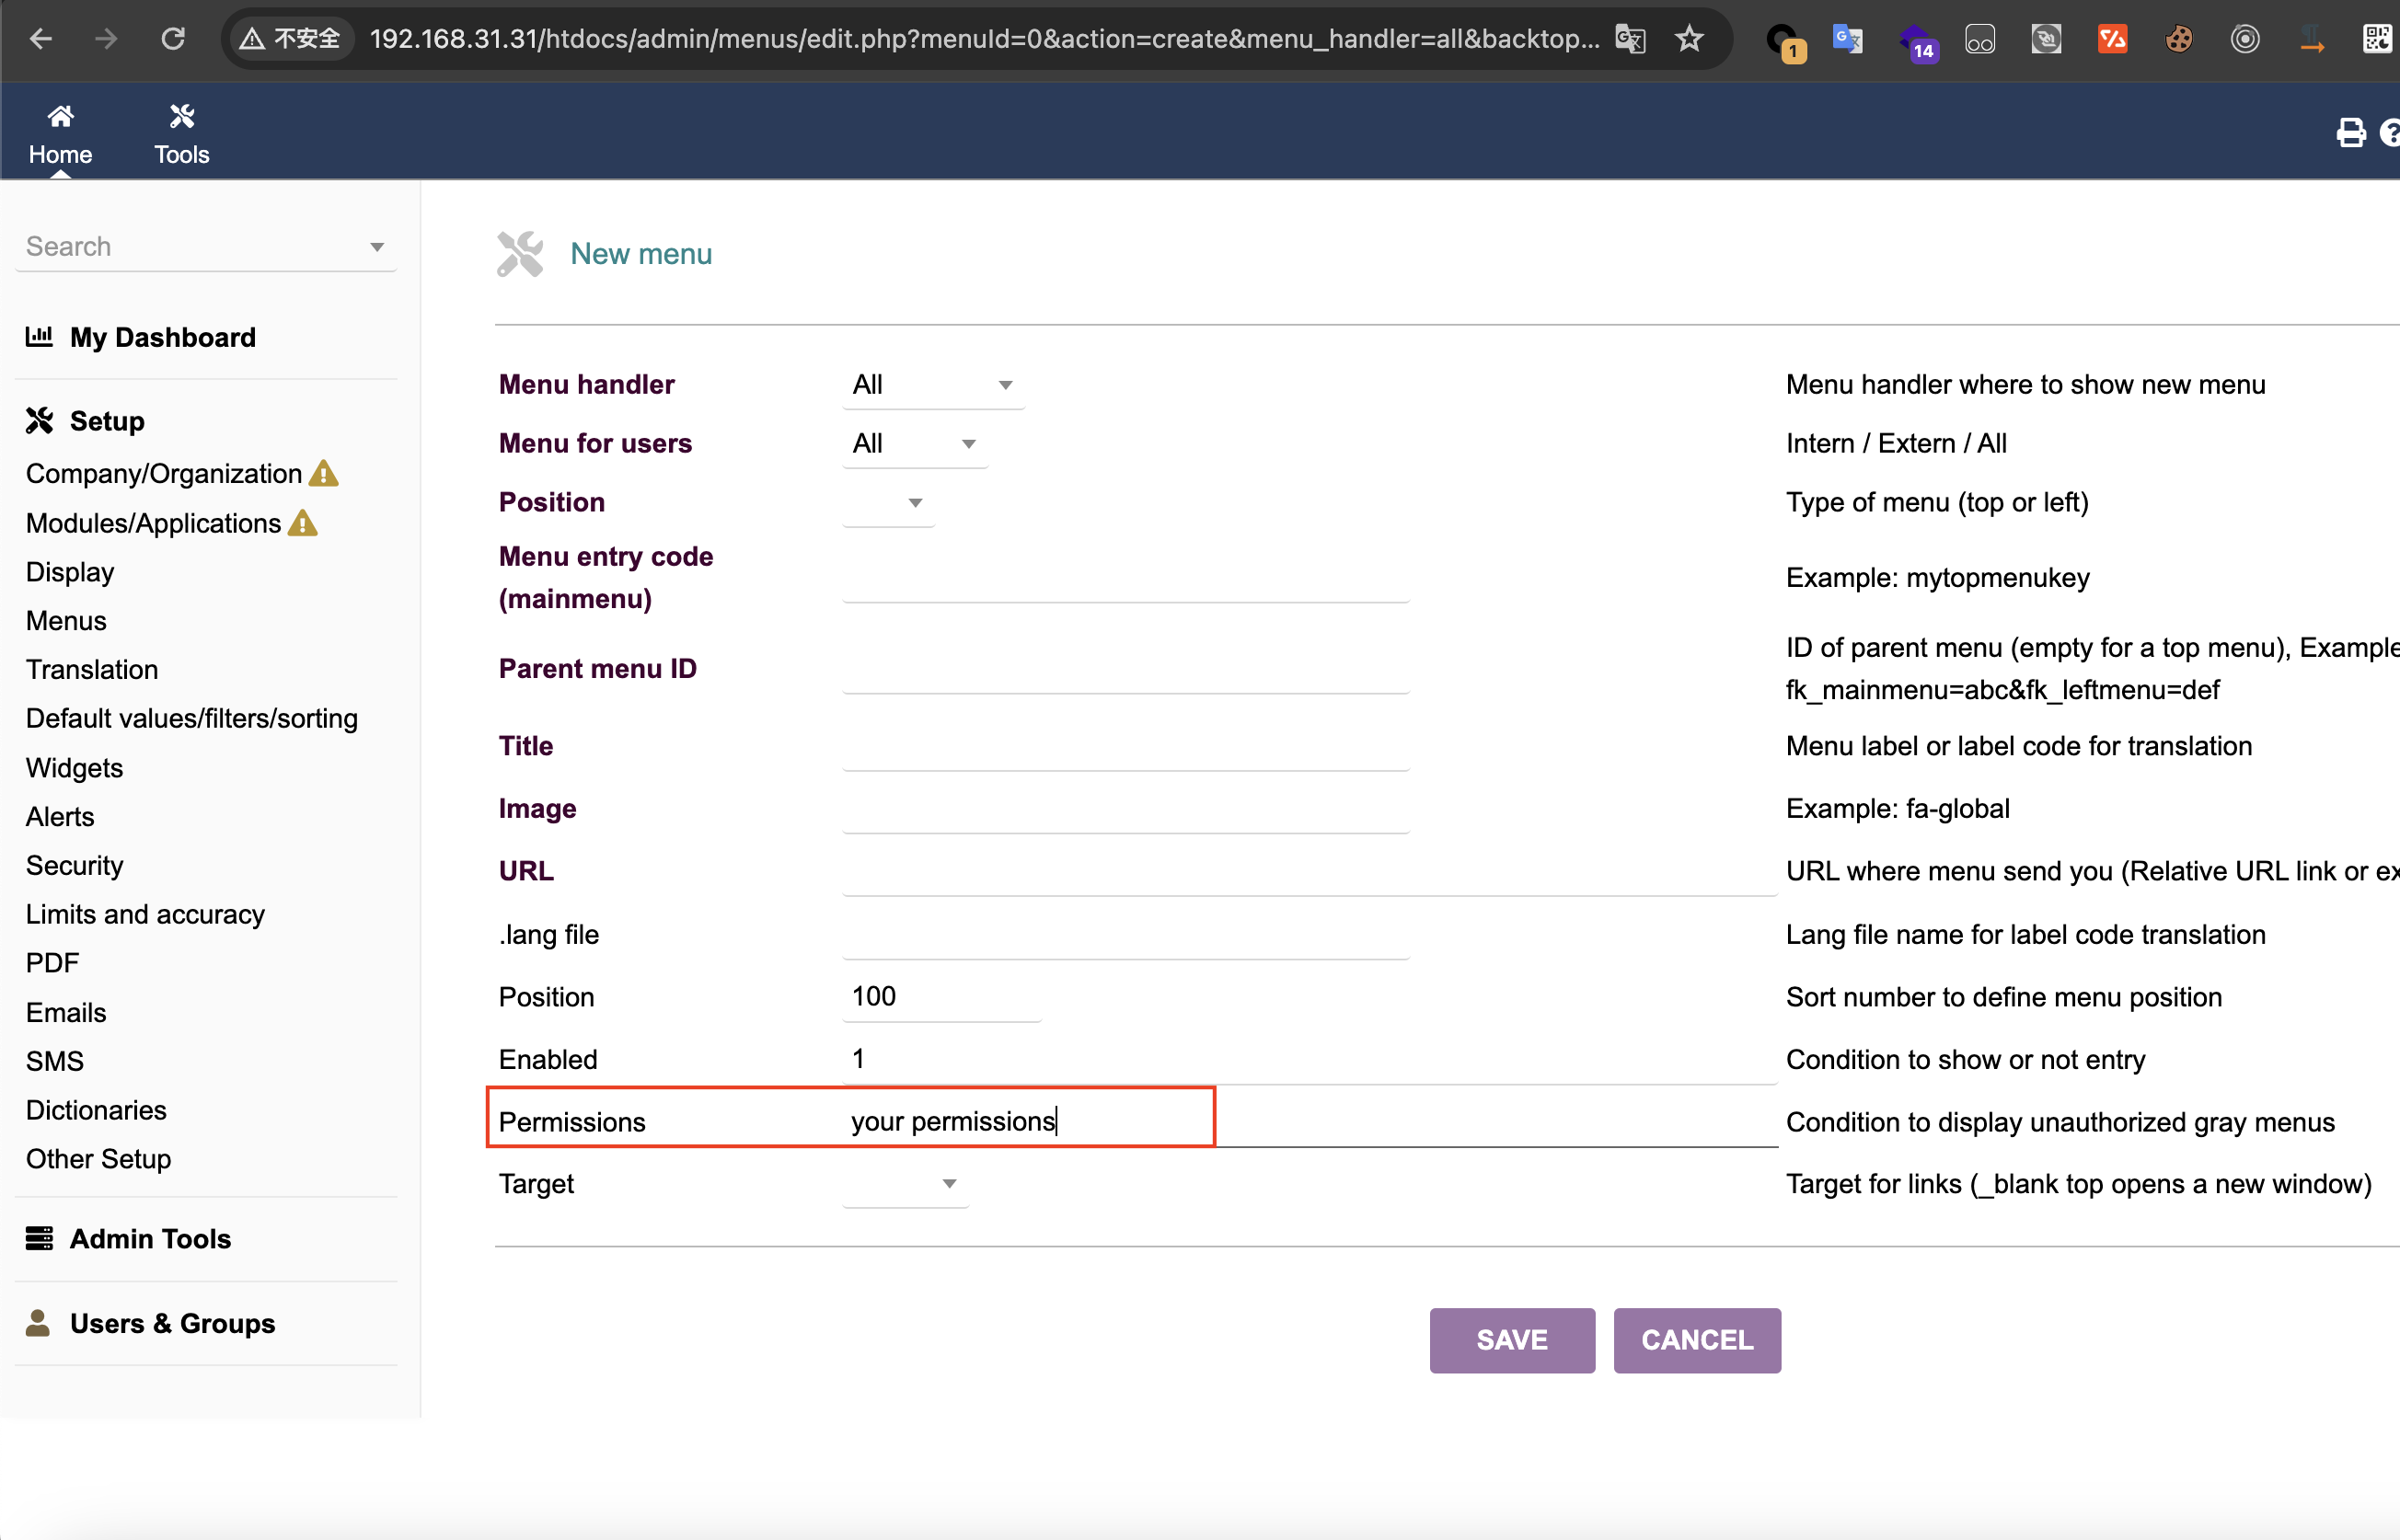 This is the trigger point of the vulnerabili…
-
High 7.5
File Download - Moderately critical - Access bypass - SA-CONTRIB-2025-089
Missing Authorization vulnerability in Drupal File Download allows Forceful Browsing.This issue affects File Download: from 0.0.0 before 1.9.0, from 2.0.0 before 2.0.1.
-
Medium 6.1
Real-time SEO for Drupal - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-091
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Real-time SEO for Drupal allows Cross-Site Scripting (XSS).This issue affects Real-time SEO for Drupal: from 2.0.0 before 2.2.0.
-
Medium 6.1
Block Attributes - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-090
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Block Attributes allows Cross-Site Scripting (XSS).This issue affects Block Attributes: from 0.0.0 before 1.1.0, from 2.0.0 before 2.0.1.
-
Medium 6.1
Cookies Addons - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-087
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Cookies Addons allows Cross-Site Scripting (XSS).This issue affects Cookies Addons: from 1.0.0 before 1.2.4.
-
Critical 9.8
Mail Login - Critical - Access bypass - SA-CONTRIB-2025-088
Improper Restriction of Excessive Authentication Attempts vulnerability in Drupal Mail Login allows Brute Force.This issue affects Mail Login: from 3.0.0 before 3.2.0, from 4.0.0 before 4.2.0.
-
High 8.1
nova-tiptap has an Unauthenticated Arbitrary File Upload Vulnerability
marshmallow-packages/nova-tiptap is a rich text editor for Laravel Nova based on tiptap. Prior to 5.7.0, a vulnerability was discovered in the marshmallow-packages/nova-tiptap Laravel Nova package that allows unauthenticated users to upload arbitrary files to…
-
Critical 9.8
simogeo/filemanager arbitrary file upload vulnerability
An arbitrary file upload vulnerability in the is_allowed_file_type() function of Filemanager v2.3.0 allows attackers to execute arbitrary code via uploading a crafted PHP file.
-
Medium 6.5
Filemanager is vulnerable to Relative Path Traversal through filemanager.php
An issue in Filemanager v2.5.0 and below allows attackers to execute a directory traversal via sending a crafted HTTP request to the filemanager.php endpoint.
-
Critical 9.2
Livewire vulnerable to remote command execution during property update hydration
Livewire is a full-stack framework for Laravel. In Livewire v3 up to and including v3.6.3, a vulnerability allows unauthenticated attackers to achieve remote command execution in specific scenarios. The issue stems from how certain component property updates …
KEV Mar 20, 2026 -
Critical 10.0
LaRecipe is vulnerable to Server-Side Template Injection attacks
LaRecipe is an application that allows users to create documentation with Markdown inside a Laravel app. Versions prior to 2.8.1 are vulnerable to Server-Side Template Injection (SSTI), which could potentially lead to Remote Code Execution (RCE) in vulnerable…
-
Medium 4.9
phpThumb is vulnerable to Command Injection through its gif_outputAsJpeg function
gif_outputAsJpeg in phpThumb through 1.7.23 allows phpthumb.gif.php OS Command Injection via a crafted parameter value. This is fixed in 1.7.23-202506081709.
-
High 8.7
DynamicPageList3 exposes hidden/suppressed usernames
The DynamicPageList3 extension is a reporting tool for MediaWiki, listing category members and intersections with various formats and details. Several #dpl parameters can leak usernames that have been hidden using revision deletion, suppression, or the hideus…
-
Medium 5.3
Config Pages Viewer - Critical - Access bypass - SA-CONTRIB-2025-086
Missing Authentication for Critical Function vulnerability in Drupal Config Pages Viewer allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects Config Pages Viewer: from 0.0.0 before 1.0.4.
-
Medium 6.5
Two-factor Authentication (TFA) - Less critical - Access bypass - SA-CONTRIB-2025-085
Privilege Defined With Unsafe Actions vulnerability in Drupal Two-factor Authentication (TFA) allows Exploiting Incorrectly Configured Access Control Security Levels.This issue affects Two-factor Authentication (TFA): from 0.0.0 before 1.11.0.
-
Low 3.5
Cockpit save cross site scripting
A vulnerability was found in Cockpit up to 2.11.3. It has been rated as problematic. This issue affects some unknown processing of the file /system/users/save. The manipulation of the argument name/email leads to cross site scripting. The attack may be initia…
-
High 8.6
Citizen Short Description stored XSS vulnerability through wikitext
Short Description is a MediaWiki extension that provides local short description support. In version 4.0.0, short descriptions are not properly sanitized before being inserted as HTML using mw.util.addSubtitle, allowing any user to insert arbitrary HTML into …
-
High 7.5CVE-2025-34086 Public exploit
Bolt CMS Authenticated Remote Code Execution via Profile Injection and File Rename
Bolt CMS versions 3.7.0 and earlier contain a chain of vulnerabilities that together allow an authenticated user to achieve remote code execution. A user with valid credentials can inject arbitrary PHP code into the displayname field of the user profile, whic…
-
High 8.6
Citizen stored XSS vulnerability through short descriptions
Citizen is a MediaWiki skin that makes extensions part of the cohesive experience. From versions 1.9.4 to before 3.4.0, short descriptions set via the ShortDescription extension are inserted as raw HTML by the Citizen skin, allowing any user to insert arbitra…
-
High 8.6
Citizen is vulnerable to stored XSS attack in the legacy search bar
Citizen is a MediaWiki skin that makes extensions part of the cohesive experience. From versions 1.9.4 to before 3.4.0, page descriptions are inserted into raw HTML without proper sanitization by the Citizen skin when using the old search bar. Any user with p…
-
Medium 6.1CVE-2025-34076 Public exploit
Microweber CMS Authenticated Local File Inclusion via Backup API
An authenticated local file inclusion vulnerability exists in Microweber CMS versions <= 1.2.11 through misuse of the backup management API. Authenticated users can abuse the /api/BackupV2/upload and /api/BackupV2/download endpoints to read arbitrary files fr…
-
High 8.6
TabberNeue vulnerable to Stored XSS through wikitext
TabberNeue is a MediaWiki extension that allows the wiki to create tabs. Starting in version 3.0.0 and prior to version 3.1.1, any user can insert arbitrary HTMLinto the DOM by inserting a payload into any allowed attribute of the `<tabber>` tag. Version 3.1.…
-
Medium 6.3
raspap-webgui has a Directory Traversal vulnerability
RaspAP raspap-webgui 3.3.1 is vulnerable to Directory Traversal in ajax/networking/get_wgkey.php. An authenticated attacker can send a crafted POST request with a path traversal payload in the `entity` parameter to overwrite arbitrary files writable by the we…
-
Medium 6.3
juzaweb CMS Add New Themes Page install improper authorization
A vulnerability classified as critical was found in juzaweb CMS 3.4.2. Affected by this vulnerability is an unknown functionality of the file /admin-cp/theme/install of the component Add New Themes Page. The manipulation leads to improper authorization. The a…
-
Medium 6.3
juzaweb CMS Import Page imports improper authorization
A vulnerability classified as critical has been found in juzaweb CMS 3.4.2. Affected is an unknown function of the file /admin-cp/imports of the component Import Page. The manipulation leads to improper authorization. It is possible to launch the attack remot…
-
Medium 5.4
Paragraphs table - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-084
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Paragraphs table allows Cross-Site Scripting (XSS).This issue affects Paragraphs table: from 2.0.0 before 2.0.5.
-
Medium 5.4
Simple XML sitemap - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-083
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Simple XML sitemap allows Cross-Site Scripting (XSS).This issue affects Simple XML sitemap: from 0.0.0 before 4.2.2.
-
Medium 4.8
Enterprise MFA - TFA for Drupal - Critical - Access bypass - SA-CONTRIB-2025-082
Authentication Bypass Using an Alternate Path or Channel vulnerability in Drupal Enterprise MFA - TFA for Drupal allows Authentication Bypass.This issue affects Enterprise MFA - TFA for Drupal: from 0.0.0 before 4.8.0, from 5.2.0 before 5.2.1, from 0.0.0 befo…
-
Medium 6.1
CKEditor5 Youtube - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-081
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal CKEditor5 Youtube allows Cross-Site Scripting (XSS).This issue affects CKEditor5 Youtube: from 0.0.0 before 1.0.3.
-
Medium 4.3
Klaro Cookie & Consent Management - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-080
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Klaro Cookie & Consent Management allows Cross-Site Scripting (XSS).This issue affects Klaro Cookie & Consent Management: from 0.0.0 before 3.0.7.
-
Medium 6.1
GLightbox - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-078
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal GLightbox allows Cross-Site Scripting (XSS).This issue affects GLightbox: from 0.0.0 before 1.0.16.
-
Medium 6.1
Toc.js - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-077
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal Toc.Js allows Cross-Site Scripting (XSS).This issue affects Toc.Js: from 0.0.0 before 3.2.1.
-
Medium 4.3
Adobe Commerce | Incorrect Authorization (CWE-863)
Adobe Commerce versions 2.4.8, 2.4.7-p5, 2.4.6-p10, 2.4.5-p12, 2.4.4-p13 and earlier are affected by an Incorrect Authorization vulnerability that could result in a Security feature bypass. An attacker could leverage this vulnerability to bypass security meas…
-
Low 2.7
Adobe Commerce | Incorrect Authorization (CWE-863)
Adobe Commerce versions 2.4.8, 2.4.7-p5, 2.4.6-p10, 2.4.5-p12, 2.4.4-p13 and earlier are affected by an Incorrect Authorization vulnerability that could result in a Security feature bypass. A high-privileged attacker could leverage this vulnerability to bypas…
-
Medium 4.2
Moodle Session Fixation allows unauthenticated users to hijack sessions via sesskey parameter
A session fixation vulnerability in Moodle 3.x through 3.11.18 allows unauthenticated attackers to hijack user sessions via the sesskey parameter. The sesskey can be obtained without authentication and reused within the OAuth2 login flow, resulting in the vic…
-
Critical 10.0
Pterodactyl Panel Allows Unauthenticated Arbitrary Remote Code Execution
Pterodactyl is a free, open-source game server management panel. Prior to version 1.11.11, using the /locales/locale.json with the locale and namespace query parameters, a malicious actor is able to execute arbitrary code without being authenticated. With the…
-
Low 3.9
handcraftedinthealps goodby-csv Potential Gadget Chain allowing Remote Code Execution
handcraftedinthealps goodby-csv is a highly memory efficient, flexible and extendable open-source CSV import/export library. Prior to 1.4.3, goodby-csv could be used as part of a chain of methods that is exploitable when an insecure deserialization vulnerabil…
-
High 8.6
COOKiES Consent Management - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-076
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal COOKiES Consent Management allows Cross-Site Scripting (XSS).This issue affects COOKiES Consent Management: from 0.0.0 before 1.2.15.
-
High 8.6
COOKiES Consent Management - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-075
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal COOKiES Consent Management allows Cross-Site Scripting (XSS).This issue affects COOKiES Consent Management: from 0.0.0 before 1.2.15.
-
High 7.3
etracker - Moderately critical - Cross Site Scripting - SA-CONTRIB-2025-074
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal etracker allows Cross-Site Scripting (XSS).This issue affects etracker: from 0.0.0 before 3.1.0.