
13,612 results · Clear filters · Feed
-
High 7.5
Apache JSPWiki: Cross-Site Scripting (XSS) in JSPWiki Header Link processing
A carefully crafted request when creating a header link using the wiki markup syntax, which could allow the attacker to execute javascript in the victim's browser and get some sensitive information about the victim. Further research by the JSPWiki team showed…
-
High 7.1
GitProxy is susceptible to a hidden commits injection attack
GitProxy is an application that stands between developers and a Git remote endpoint. In versions 1.19.1 and below, attackers can inject extra commits into the pack sent to GitHub, commits that aren’t pointed to by any branch. Although these “hidden” commits n…
-
High 8.2
GitProxy is vulnerable to a new branch approval exploit
GitProxy is an application that stands between developers and a Git remote endpoint. In versions 1.19.1 and below, attackers can exploit the way GitProxy handles new branch creation to bypass the approval of prior commits on the parent branch. The vulnerabili…
-
High 7.0
GitProxy is vulnerable to a packfile parsing exploit
GitProxy is an application that stands between developers and a Git remote endpoint (e.g., github.com). In versions 1.19.1 and below, an attacker can craft a malicious Git packfile to exploit the PACK signature detection in the parsePush.ts file. By embedding…
-
High 8.3
GitProxy bypasses approvals when pushing multiple branches
GitProxy is an application that stands between developers and a Git remote endpoint (e.g., github.com). Versions 1.19.1 and below allow users to push to remote repositories while bypassing policies and explicit approvals. Since checks and plugins are skipped,…
-
High 7.5
vproxy is vulnerable to a divide by zero DoS attack
vproxy is an HTTP/HTTPS/SOCKS5 proxy server. In versions 2.3.3 and below, untrusted data is extracted from the user-controlled HTTP Proxy-Authorization header and passed to Extension::try_from and flows into parse_ttl_extension where it is parsed as a TTL val…
-
High 7.6
Config Pages - Moderately critical - Access bypass - SA-CONTRIB-2025-093
Missing Authorization vulnerability in Drupal Config Pages allows Forceful Browsing. This issue affects Config Pages: from 0.0.0 before 2.18.0.
-
High 7.1
Keycloak: phishing attack via email verification step in first login flow
A flaw was found in Keycloak. When an authenticated attacker attempts to merge accounts with another existing account during an identity provider (IdP) login, the attacker will subsequently be prompted to "review profile" information. This vulnerability allow…
-
High 8.1CVE-2025-45346 Public exploit
Bacula-web SQL Injection Vulnerability
SQL Injection vulnerability in Bacula-web before v.9.7.1 allows a remote attacker to execute arbitrary code via a crafted HTTP GET request.
-
High 8.6
Unexpected command execution in untrusted VCS repositories in cmd/go
The go command may execute unexpected commands when operating in untrusted VCS repositories. This occurs when possibly dangerous VCS configuration is present in repositories. This can happen when a repository was fetched via one VCS (e.g. Git), but contains m…
-
High 7.3
Couchbase Sync Gateway shows cleartext passwords in redacted and unredacted output
An issue was discovered in Couchbase Sync Gateway before 3.2.6. In sgcollect_info_options.log and sync_gateway.log, there are cleartext passwords in redacted and unredacted output.
-
High 7.2
Bugsink is vulnerable to Path Traversal attacks via event_id in ingestion
Bugsink is a self-hosted error tracking service. In versions 1.4.2 and below, 1.5.0 through 1.5.4, 1.6.0 through 1.6.3, and 1.7.0 through 1.7.3, ingestion paths construct file locations directly from untrusted event_id input without validation. A specially cr…
-
High 7.6CVE-2025-5120 EPSS 31%
Sandbox Escape Vulnerability in huggingface/smolagents
A sandbox escape vulnerability was identified in huggingface/smolagents version 1.14.0, allowing attackers to bypass the restricted execution environment and achieve remote code execution (RCE). The vulnerability stems from the local_python_executor.py module…
-
High 8.8
Linkify 4.3.1 - Prototype Pollution & HTML Attribute Injection (XSS)
Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution') vulnerability in Linkify (linkifyjs) allows XSS Targeting HTML Attributes and Manipulating User-Controlled Variables.This issue affects Linkify: from 4.3.1 before 4.3.2.
-
High 8.3
HAX CMS Backend Lacks Comprehensive Authorization Checks
HAX CMS allows you to manage your microsite universe with PHP or NodeJs backends. In versions 11.0.13 and below of haxcms-nodejs and versions 11.0.8 and below of haxcms-php, API endpoints do not perform authorization checks when interacting with a resource. B…
-
High 8.7
skops' MethodNode can access unexpected object fields through dot notation, leading to arbitrary code execution at load time
skops is a Python library which helps users share and ship their scikit-learn based models. Versions 0.11.0 and below contain an inconsistency in MethodNode, which can be exploited to access unexpected object fields through dot notation. This can be used to a…
-
High 8.7
skops' Inconsistent Trusted Type Validation Enables Hidden `operator` Methods Execution
skops is a Python library which helps users share and ship their scikit-learn based models. Versions 0.11.0 and below contain a inconsistency in the OperatorFuncNode which can be exploited to hide the execution of untrusted operator methods. This can then be …
-
High 8.6
XWiki Platform's searchDocuments API allows for SQL injection
XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. In versions between 17.0.0-rc1 to 17.2.2 and versions 16.10.5 and below, it's possible to execute any SQL query in Oracle by using the function like DBMS_…
-
High 7.5
NULL Pointer Dereference in µD3TN
NULL Pointer Dereference in µD3TN via non-singleton destination Endpoint Identifier allows remote attacker to reliably cause DoS
-
High 8.9
eKuiper API endpoints handling SQL queries with user-controlled table names.
LF Edge eKuiper is a lightweight IoT data analytics and stream processing engine running on resource-constraint edge devices. In versions before 2.2.1, there is a critical SQL Injection vulnerability in the getLast API functionality of the eKuiper project. Th…
-
High 8.7CVE-2025-6998 Public exploit
Calibre Web 0.6.24 & Autocaliweb 0.7.0 - ReDoS
ReDoS in strip_whitespaces() function in cps/string_helper.py in Calibre Web and Autocaliweb allows unauthenticated remote attackers to cause denial of service via specially crafted username parameter that triggers catastrophic backtracking during login. This…
-
High 7.5
ImageMagick has XMP profile write that triggers hang due to unbounded loop
ImageMagick is free and open-source software used for editing and manipulating digital images. In versions prior to 7.1.2-0, infinite lines occur when writing during a specific XMP file conversion command. Version 7.1.2-0 fixes the issue.
-
High 7.6
COOKiES Consent Management - Moderately critical - Cross-site Scripting - SA-CONTRIB-2025-092
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Drupal COOKiES Consent Management allows Cross-Site Scripting (XSS).This issue affects COOKiES Consent Management: from 0.0.0 before 1.2.16.
-
High 7.8
fastapi-guard patch contains bypassable RegEx
fastapi-guard is a security library for FastAPI that provides middleware to control IPs, log requests, detect penetration attempts and more. In version 3.0.1, the regular expression patched to mitigate the ReDoS vulnerability by limiting the length of string …
-
High 8.2
private-ip vulnerable to Server-Side Request Forgery
All versions of the package private-ip are vulnerable to Server-Side Request Forgery (SSRF) where an attacker can provide an IP or hostname that resolves to a multicast IP address (224.0.0.0/4) which is not included as part of the private IP ranges in the pac…
-
High 7.5
files-bucket-server vulnerable to Directory Traversal
All versions of the package files-bucket-server are vulnerable to Directory Traversal where an attacker can traverse the file system and access files outside of the intended directory.
-
High 8.8
Aim vulnerable to Cross-site Scripting
Cross-site Scripting (XSS) in aimhubio Aim 3.28.0 allows remote attackers to execute arbitrary JavaScript in victims browsers via malicious Python code submitted to the /api/reports endpoint, which is interpreted and executed by Pyodide when the report is vie…
-
High 7.1
authentik has an insufficient check for account active status during OAuth/SAML authentication
authentik is an open-source Identity Provider that emphasizes flexibility and versatility, with support for a wide set of protocols. In versions 2025.4.4 and earlier, as well as versions 2025.6.0-rc1 through 2025.6.3, deactivated users who registered through …
-
High 7.7
Kyverno's Improper JMESPath Variable Evaluation Leads to Denial of Service
Kyverno is a policy engine designed for cloud native platform engineering teams. In versions 1.14.1 and below, a Denial of Service (DoS) vulnerability exists due to improper handling of JMESPath variable substitutions. Attackers with permissions to create or …
-
High 7.5
pyLoad has Path Traversal Vulnerability in json/upload Endpoint that allows Arbitrary File Write
pyLoad is a free and open-source Download Manager written in pure Python. In version 0.5.0b3.dev89, an authenticated path traversal vulnerability exists in the /json/upload endpoint of pyLoad. By manipulating the filename of an uploaded file, an attacker can …
-
High 7.5
LibreNMS has Authenticated Local File Inclusion in ajax_form.php that Allows RCE
LibreNMS is an auto-discovering PHP/MySQL/SNMP based network monitoring which includes support for a wide range of network hardware and operating systems. LibreNMS versions 25.6.0 and below contain an architectural vulnerability in the ajax_form.php endpoint …
-
High 7.3
NodeJS version of the HAX CMS application is distributed with Default Secrets
HAX CMS NodeJS allows users to manage their microsite universe with a NodeJS backend. Versions 11.0.9 and below were distributed with hardcoded default credentials for the user and superuser accounts. Additionally, the application has default private keys for…
-
High 7.1
HAX CMS NodeJs's Improper Error Handling Leads to Denial of Service
HAX CMS NodeJs allows users to manage their microsite universe with a NodeJs backend. In versions 11.0.8 and below, the HAX CMS NodeJS application crashes when an authenticated attacker provides an API request lacking required URL parameters. This vulnerabili…
-
High 7.2
HAX CMS NodeJs's Disabled Content Security Policy Enables Cross-Site Scripting
HAX CMS NodeJs allows users to manage their microsite universe with a NodeJs backend. In versions 11.0.7 and below, the NodeJS version of HAX CMS has a disabled Content Security Policy (CSP). This configuration is insecure for a production application because…
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 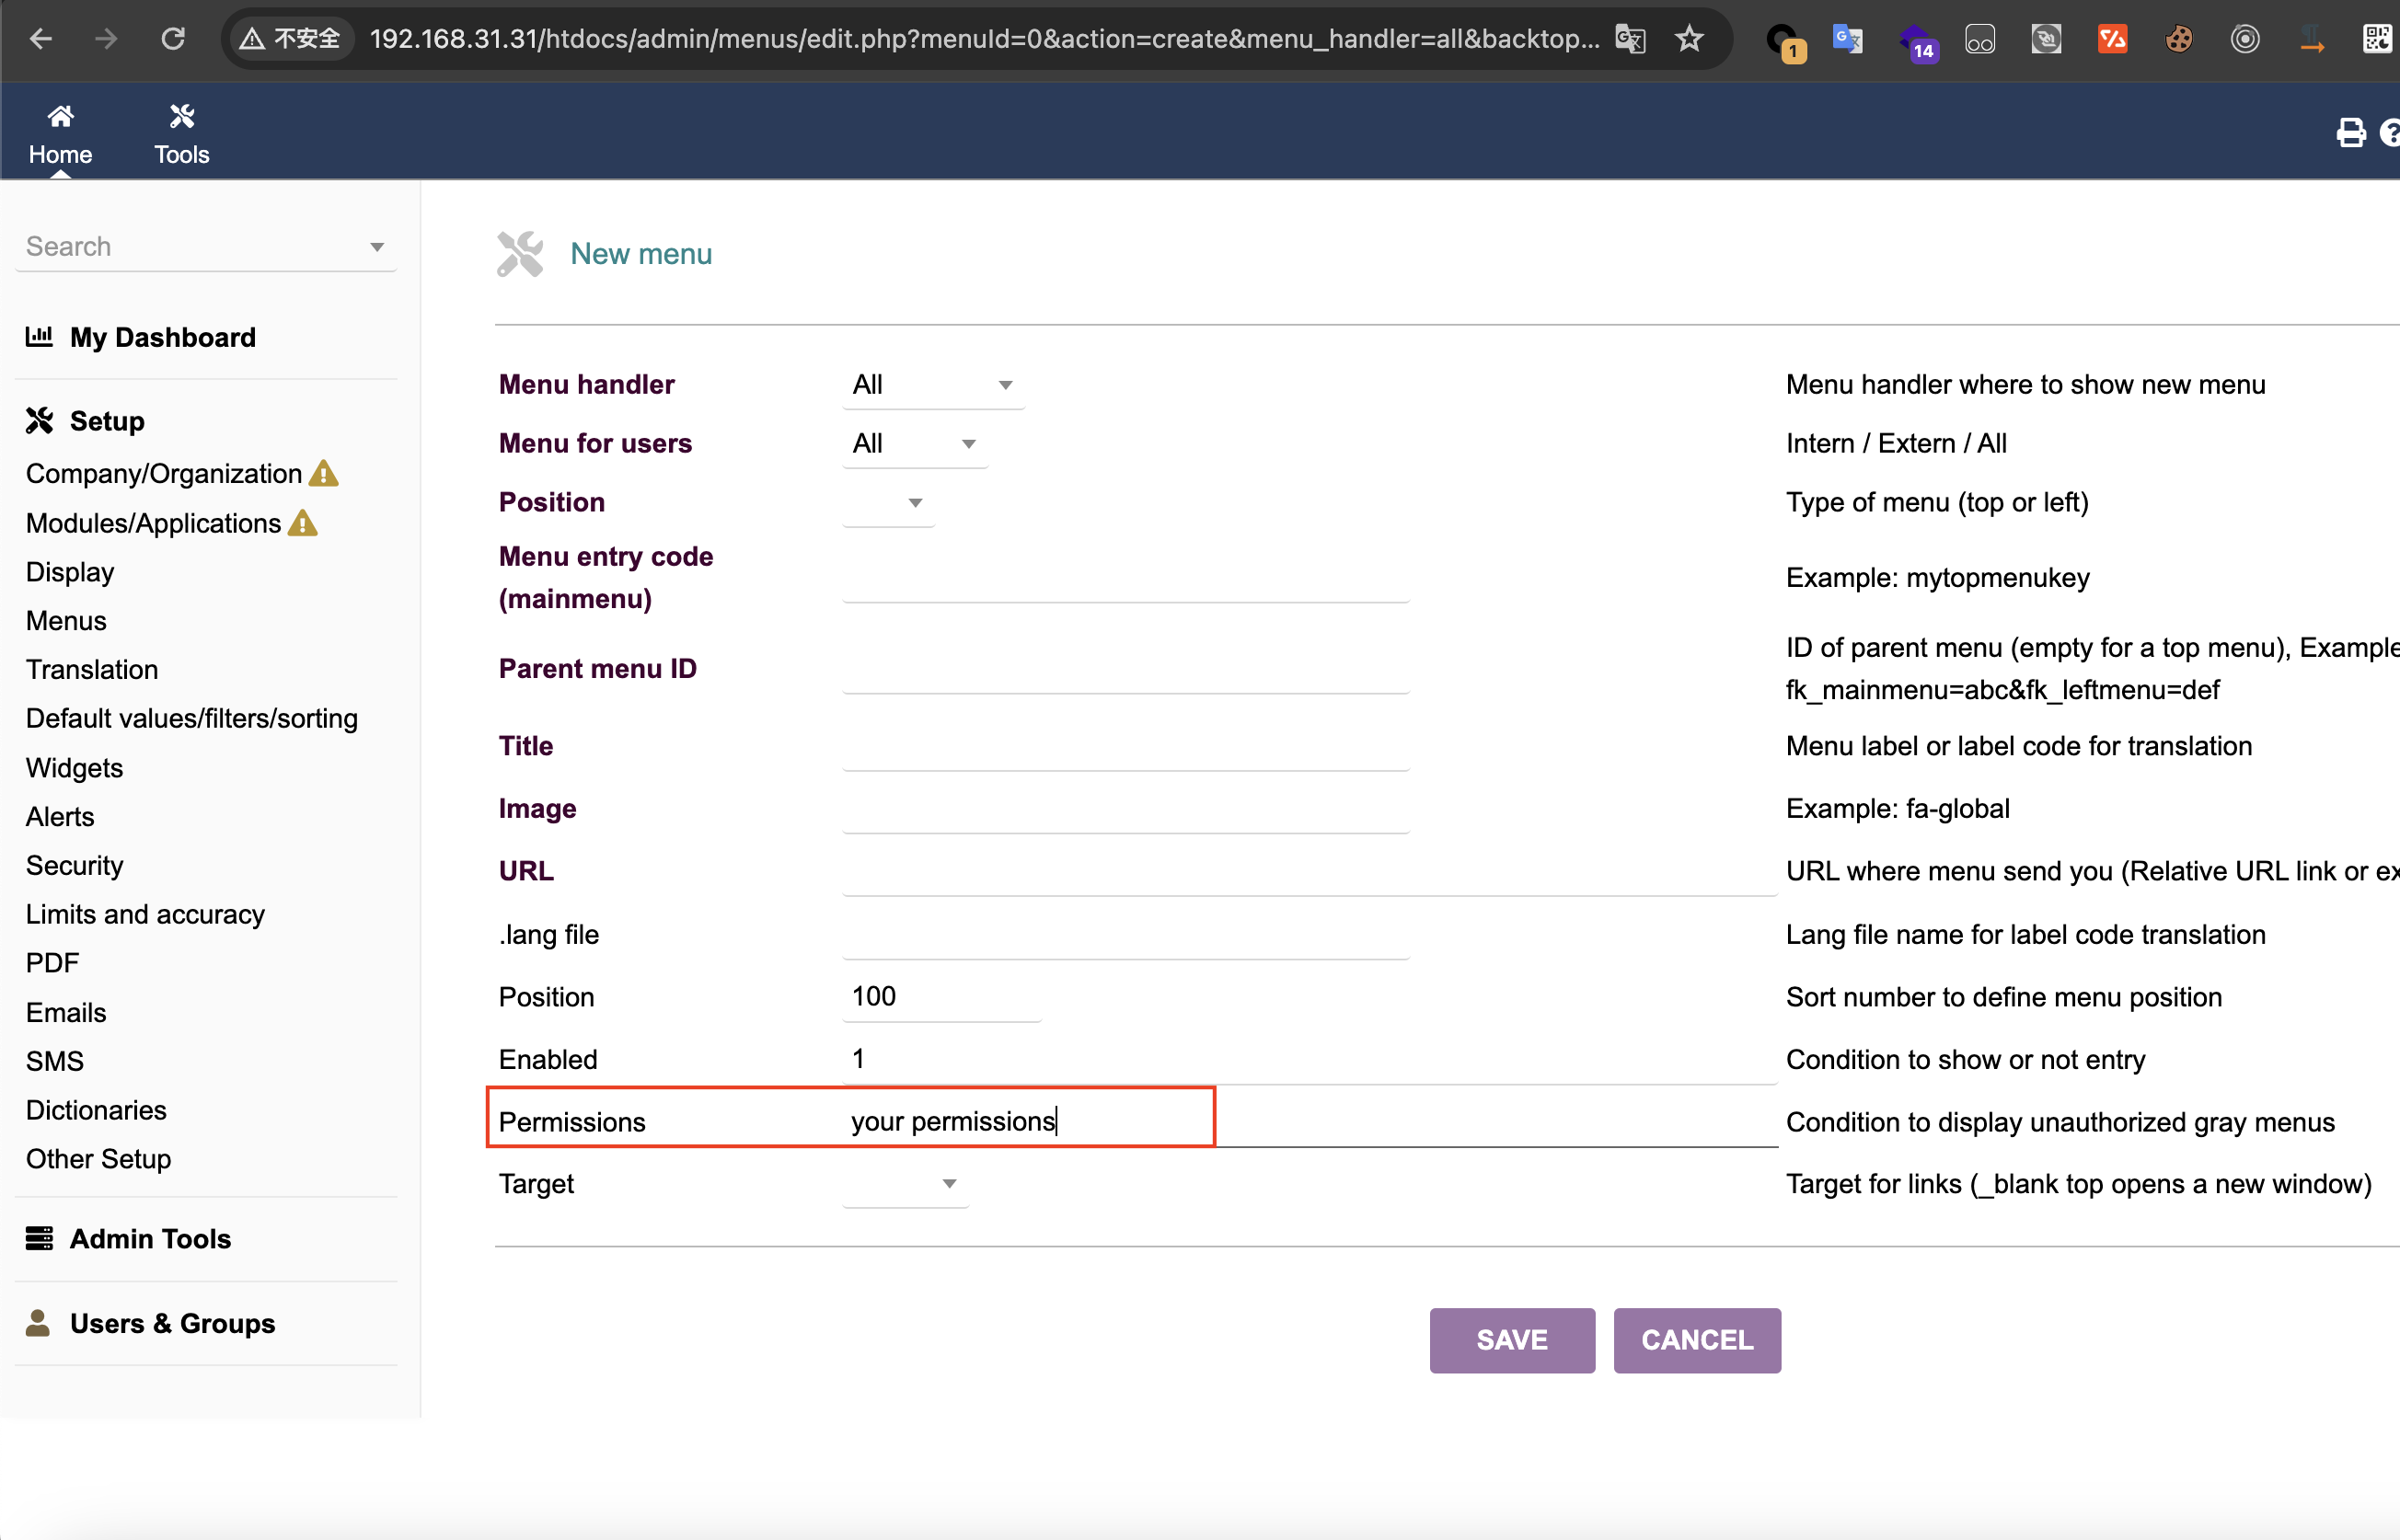 This is the trigger point of the vulnerabili…
-
High —
RageAgainstThePixel/setup-steamcmd leaked authentication token in job output logs
### Summary Log output includes authentication token that provides full account access ### Details The post job action prints the contents of `config/config.vdf` which holds the saved authentication token and can be used to sign in on another machine. This me…
-
High —
buildalon/setup-steamcmd leaked authentication token in job output logs
### Summary Log output includes authentication token that provides full account access ### Details The post job action prints the contents of `config/config.vdf` which holds the saved authentication token and can be used to sign in on another machine. This me…
-
High 8.1
nova-tiptap has an Unauthenticated Arbitrary File Upload Vulnerability
marshmallow-packages/nova-tiptap is a rich text editor for Laravel Nova based on tiptap. Prior to 5.7.0, a vulnerability was discovered in the marshmallow-packages/nova-tiptap Laravel Nova package that allows unauthenticated users to upload arbitrary files to…
-
High —
Alchemy Non-SMA and Webauthn Account Security Advisory
### Impact A potential security issue has been mitigated on old account deployment functions from the factory. Smart wallets in use on all existing supported networks are not impacted. ### Patches Please direct creation of new wallets to either `createSemiMod…
-
High 7.5CVE-2025-53832 EPSS 11%
@translated/lara-mcp vulnerable to command injection in import_tmx tool
Lara Translate MCP Server is a Model Context Protocol (MCP) Server for Lara Translate API. Versions 0.0.11 and below contain a command injection vulnerability which exists in the @translated/lara-mcp MCP Server. The vulnerability is caused by the unsanitized …