
Weakness (CWE)
CWE-98: PHP Remote File Inclusion"
The PHP application receives input from an upstream component, but it does not restrict or incorrectly restricts the input before its usage in "require," "include," or similar functions.
How to prevent it (8 mitigations)
-
Architecture and Design
Use a vetted library or framework that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid [REF-1482].
-
Architecture and Design
When the set of acceptable objects, such as filenames or URLs, is limited or known, create a mapping from a set of fixed input values (such as numeric IDs) to the actual filenames or URLs, and reject all other inputs.
For example, ID 1 could map to "inbox.txt" and ID 2 could map to "profile.txt". Features such as the ESAPI AccessReferenceMap [REF-185] provide this capability.
-
Architecture and Design
For any security checks that are performed on the client side, ensure that these checks are duplicated on the server side, in order to avoid CWE-602. Attackers can bypass the client-side checks by modifying values after the checks have been performed, or by changing the client to remove the client-side checks entirely. Then, these modified values would be submitted to the server.
-
Architecture and Design, Operation
Run the code in a "jail" or similar sandbox environment that enforces strict boundaries between the process and the operating system. This may effectively restrict which files can be accessed in a particular directory or which commands can be executed by the software.
OS-level examples include the Unix chroot jail, AppArmor, and SELinux. In general, managed code may provide some protection. For example, java.io.FilePermission in the Java SecurityManager allows the software to specify restrictions on file operations.
This may not be a feasible solution, and it only limits the impact to the operating system; the rest of the application may still be subject to compromise.
Be careful to avoid CWE-243 and other weaknesses related to jails.
-
Architecture and Design, Operation
Run your code using the lowest privileges that are required to accomplish the necessary tasks [REF-76]. If possible, create isolated accounts with limited privileges that are only used for a single task. That way, a successful attack will not immediately give the attacker access to the rest of the software or its environment. For example, database applications rarely need to run as the database administrator, especially in day-to-day operations.
-
Implementation
Assume all input is malicious. Use an "accept known good" input validation strategy, i.e., use a list of acceptable inputs that strictly conform to specifications. Reject any input that does not strictly conform to specifications, or transform it into something that does.
When performing input validation, consider all potentially relevant properties, including length, type of input, the full range of acceptable values, missing or extra inputs, syntax, consistency across related fields, and conformance to business rules. As an example of business rule logic, "boat" may be syntactically valid because it only contains alphanumeric characters, but it is not valid if the input is only expected to contain colors such as "red" or "blue."
Do not rely exclusively on looking for malicious or malformed inputs. This is likely to miss at least one undesirable input, especially if the code's environment changes. This can give attackers enough room to bypass the intended validation. However, denylists can be useful for detecting potential attacks or determining which inputs are so malformed that they should be rejected outright.
When validating filenames, use stringent lists that limit the character set to be used. If feasible, only allow a single "." character in the filename to avoid weaknesses such as CWE-23, and exclude directory separators such as "/" to avoid CWE-36. Use a list of allowable file extensions, which will help to avoid CWE-434.
Do not rely exclusively on a filtering mechanism that removes potentially dangerous characters. This is equivalent to a denylist, which may be incomplete (CWE-184). For example, filtering "/" is insufficient protection if the filesystem also supports the use of "\" as a directory separator. Another possible error could occur when the filtering is applied in a way that still produces dangerous data (CWE-182). For example, if "../" sequences are removed from the ".../...//" string in a sequential fashion, two instances of "../" would be removed from the original string, but the remaining characters would still form the "../" string.
-
Architecture and Design, Operation
Store library, include, and utility files outside of the web document root, if possible. Otherwise, store them in a separate directory and use the web server's access control capabilities to prevent attackers from directly requesting them. One common practice is to define a fixed constant in each calling program, then check for the existence of the constant in the library/include file; if the constant does not exist, then the file was directly requested, and it can exit immediately.
This significantly reduces the chance of an attacker being able to bypass any protection mechanisms that are in the base program but not in the include files. It will also reduce the attack surface.
-
Architecture and Design, Implementation
Understand all the potential areas where untrusted inputs can enter your software: parameters or arguments, cookies, anything read from the network, environment variables, reverse DNS lookups, query results, request headers, URL components, e-mail, files, filenames, databases, and any external systems that provide data to the application. Remember that such inputs may be obtained indirectly through API calls.
Many file inclusion problems occur because the programmer assumed that certain inputs could not be modified, especially for cookies and URL components.
Source: MITRE CWE-98
1,361 results · Feed
-
Critical 9.8
WellChoose|Organization Portal System - Local File Inclusion
Organization Portal System developed by WellChoose has a Local File Inclusion vulnerability, allowing unauthenticated remote attackers to execute arbitrary code on the server.
-
Medium 6.5
A local file inclusion (LFI) vulnerability in Vedo Suite version 2024.17 allows remote authenticated attackers to read …
-
Critical 10.0CVE-2012-10025 Public exploit
WordPress Plugin Advanced Custom Fields <= 3.5.1 Remote File Inclusion
The WordPress plugin Advanced Custom Fields (ACF) version 3.5.1 and below contains a remote file inclusion (RFI) vulnerability in core/actions/export.php. When the PHP configuration directive allow_url_include is enabled (default: Off), an unauthenticated att…
-
High 7.5
Kallyas <= 4.21.0 - Authenticated (Contributor+) Local File Inclusion
The kallyas theme for WordPress is vulnerable to Local File Inclusion in all versions up to, and including, 4.21.0 via the 'TH_LatestPosts4` widget. This makes it possible for authenticated attackers, with Contributor-level access and above, to include and ex…
-
High 7.5
LibreNMS has Authenticated Local File Inclusion in ajax_form.php that Allows RCE
LibreNMS is an auto-discovering PHP/MySQL/SNMP based network monitoring which includes support for a wide range of network hardware and operating systems. LibreNMS versions 25.6.0 and below contain an architectural vulnerability in the ajax_form.php endpoint …
-
High 8.8
Dolibarr has Remote Code Execution Vulnerability (Bypass)
# Summary The Dolibarr backend provides the function of adding Menu, and supports setting permissions for the added Menu: 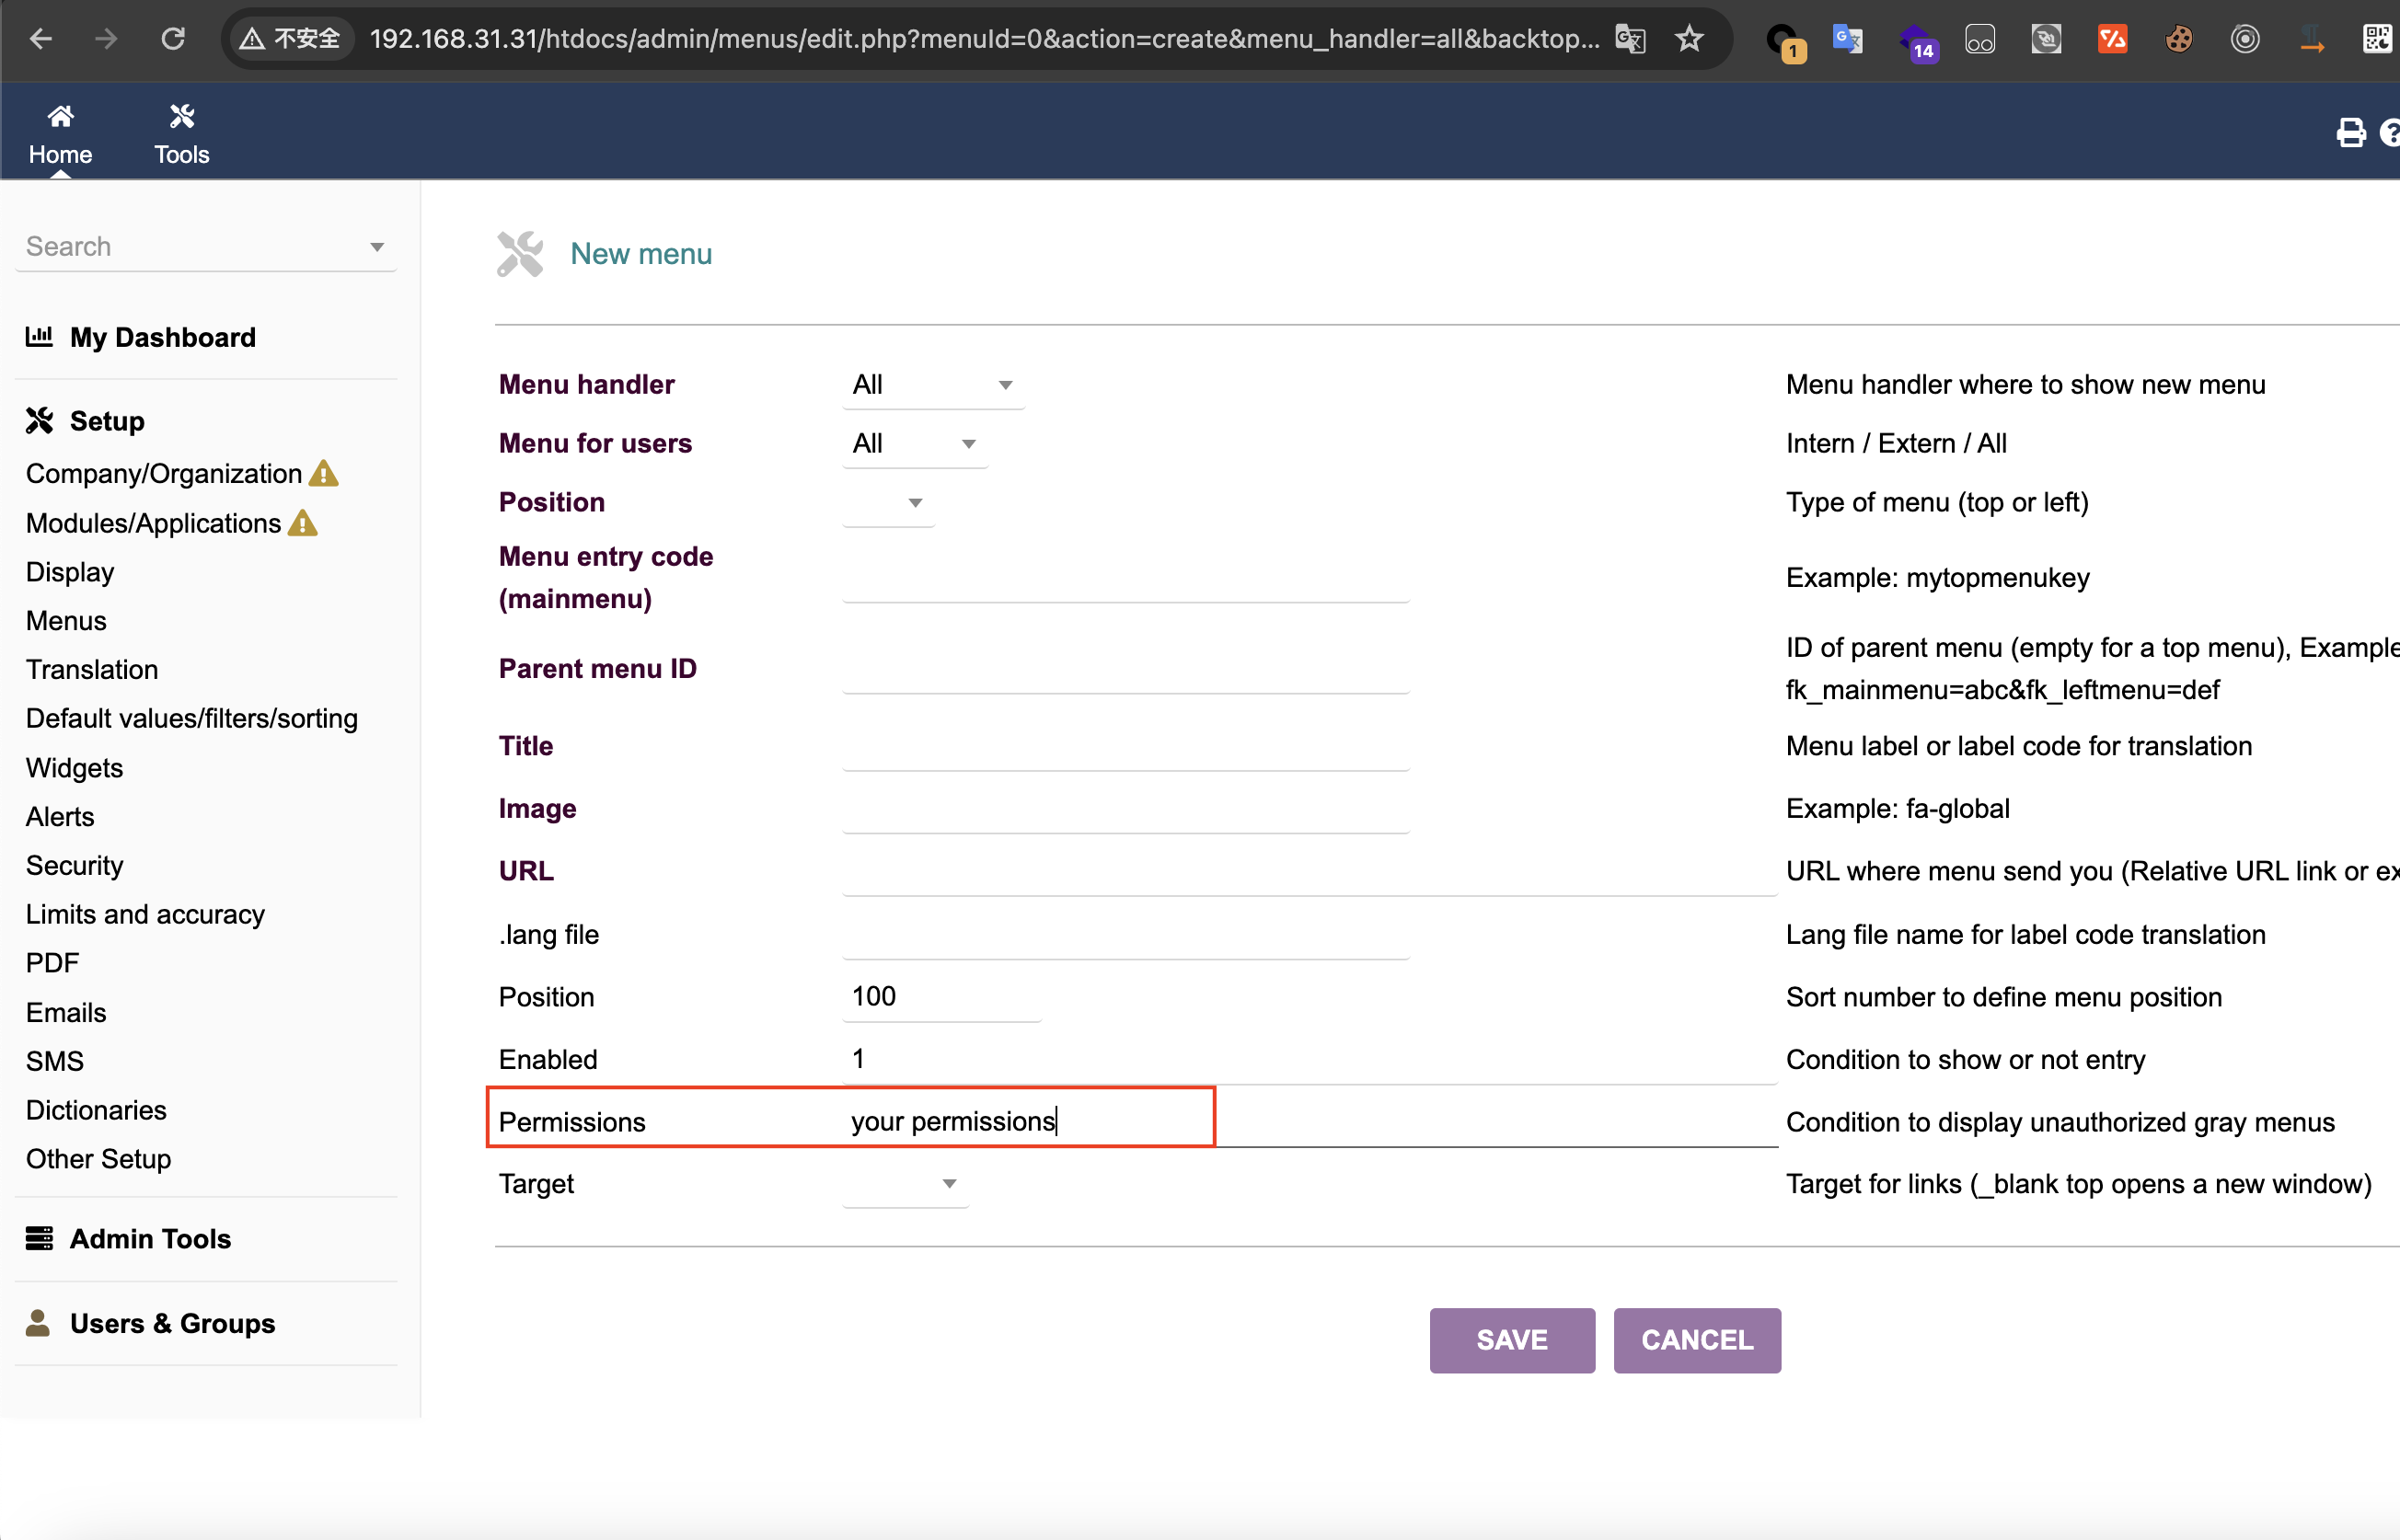 This is the trigger point of the vulnerabili…
-
Critical 9.0
Access to local file system and its content
File contents could be read from the local file system by an attacker. Additionally, malicious code could be inserted in the file, leading to a full compromise of the web application and the container it is running on. The vulnerable component is bound to the…
-
High 7.2CVE-2015-10133 Public exploit
Subscribe to Comments <= 2.1.2 - Local File Includion
The Subscribe to Comments for WordPress is vulnerable to Local File Inclusion in versions up to, and including, 2.1.2 via the Path to header value. This allows authenticated attackers, with administrative privileges and above, to include and execute arbitrary…
-
Medium 6.6
WordPress HT Contact Form 7 plugin <= 2.0.0 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in HT Plugins HT Contact Form 7 ht-contactform allows PHP Local File Inclusion.This issue affects HT Contact Form 7: from n/a through <= 2.0.…
-
High 8.8
WoodMart <= 8.2.3 - Authenticated (Contributor+) Local File Inclusion
The WoodMart plugin for WordPress is vulnerable to Local File Inclusion in all versions up to, and including, 8.2.3 via the 'layout' attribute. This makes it possible for authenticated attackers, with Contributor-level access and above, to include and execute…
-
High 8.8
Widget for Google Reviews <= 1.0.15 - Authenticated (Subscriber+) Directory Traversal to Local File Inclusion
The Widget for Google Reviews plugin for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.0.15 via the layout parameter. This makes it possible for authenticated attackers, with Subscriber-level access and above, to inclu…
-
High 7.5
WordPress PrivateContent - Mail Actions plugin <= 2.3.2 - Local File Inclusion vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in LCweb PrivateContent - Mail Actions allows PHP Local File Inclusion. This issue affects PrivateContent - Mail Actions: from n/a through 2.…
-
High 8.1
WordPress Kossy - Minimalist eCommerce WordPress Theme <= 1.45 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in ApusWP Kossy - Minimalist eCommerce WordPress Theme kossy allows PHP Local File Inclusion.This issue affects Kossy - Minimalist eCommerce …
-
High 8.1
WordPress CMSMasters Content Composer plugin < 2.5.7 - Local File Inclusion vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in cmsmasters CMSMasters Content Composer cmsmasters-content-composer allows PHP Local File Inclusion.This issue affects CMSMasters Content C…
-
High 7.5
WordPress Elessi < 6.4.1 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in NasaTheme Elessi elessi-theme allows PHP Local File Inclusion.This issue affects Elessi: from n/a through < 6.4.1.
-
High 8.1
Ads Pro Plugin - Multi-Purpose WordPress Advertising Manager <= 4.89 - Unauthenticated Local File Inclusion
The Ads Pro Plugin - Multi-Purpose WordPress Advertising Manager plugin for WordPress is vulnerable to Local File Inclusion in all versions up to, and including, 4.89 via the 'bsa_template' parameter of the `bsa_preview_callback` function. This makes it possi…
-
Critical 9.8
Ads Pro Plugin - Multi-Purpose WordPress Advertising Manager <= 4.89 - Unauthenticated Local File Inclusion to Remote Code Execution
The Ads Pro Plugin - Multi-Purpose WordPress Advertising Manager plugin for WordPress is vulnerable to Local File Inclusion which leads to Remote Code Execution in all versions up to, and including, 4.89. This is due to the presence of a SQL Injection vulnera…
-
High 7.5
WordPress Devnex Addons For Elementor plugin <= 1.0.9 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in devnex Devnex Addons For Elementor devnex-addons-for-elementor allows PHP Local File Inclusion.This issue affects Devnex Addons For Elemen…
-
High 7.5
WordPress WPB Category Slider for WooCommerce plugin <= 1.71 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in WPBean WPB Category Slider for WooCommerce wpb-woocommerce-category-slider allows PHP Local File Inclusion.This issue affects WPB Category…
-
High 7.5
WordPress Hotel Booking plugin <= 3.7 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in nicdark Hotel Booking nd-booking allows PHP Local File Inclusion.This issue affects Hotel Booking: from n/a through <= 3.7.
-
High 7.5
WordPress Gmedia Photo Gallery plugin <= 1.23.0 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in Serhii Pasyuk Gmedia Photo Gallery grand-media allows PHP Local File Inclusion.This issue affects Gmedia Photo Gallery: from n/a through <…
-
High 8.1
WordPress Zenny theme <= 1.7.5 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in BZOTheme Zenny bw-zenny allows PHP Local File Inclusion.This issue affects Zenny: from n/a through <= 1.7.5.
-
High 8.1
WordPress PrintXtore theme < 1.7.8 - Local File Inclusion vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in BZOTheme PrintXtore bw-printxtore allows PHP Local File Inclusion.This issue affects PrintXtore: from n/a through < 1.7.8.
-
High 8.1
WordPress MBStore - Digital WooCommerce WordPress Theme <= 2.3 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in snstheme MBStore - Digital WooCommerce WordPress Theme mbstore allows PHP Local File Inclusion.This issue affects MBStore - Digital WooCom…
-
High 8.1
WordPress SNS Vicky theme <= 3.7 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in snstheme SNS Vicky snsvicky allows PHP Local File Inclusion.This issue affects SNS Vicky: from n/a through <= 3.7.
-
High 8.1
WordPress SERPed.net plugin <= 4.6 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in serpednet SERPed.net serped-net allows PHP Local File Inclusion.This issue affects SERPed.net: from n/a through <= 4.6.
-
High 8.1
WordPress Puca theme <= 2.6.33 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in thembay Puca puca allows PHP Local File Inclusion.This issue affects Puca: from n/a through <= 2.6.33.
-
High 7.5
WordPress CTUsers plugin <= 1.0.0 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in Case-Themes CTUsers ctuser allows PHP Local File Inclusion.This issue affects CTUsers: from n/a through <= 1.0.0.
-
High 8.1
WordPress Greenmart theme <= 4.2.3 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in thembay Greenmart greenmart allows PHP Local File Inclusion.This issue affects Greenmart: from n/a through <= 4.2.3.
-
High 8.1
WordPress Zikzag Core plugin <= 1.4.5 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in WebGeniusLab Zikzag Core zikzag-core allows PHP Local File Inclusion.This issue affects Zikzag Core: from n/a through <= 1.4.5.
-
High 8.1
WordPress Networker theme <= 1.2.0 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in codesupplyco Networker networker allows PHP Local File Inclusion.This issue affects Networker: from n/a through <= 1.2.0.
-
High 8.1
WordPress Diza theme <= 1.3.9 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in thembay Diza diza allows PHP Local File Inclusion.This issue affects Diza: from n/a through <= 1.3.9.
-
High 8.1
WordPress RealtyElite theme <= 1.0.0 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in real-web RealtyElite realtyelite allows PHP Local File Inclusion.This issue affects RealtyElite: from n/a through <= 1.0.0.
-
High 8.1
WordPress National Weather Service Alerts plugin <= 1.3.5 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in John Russell National Weather Service Alerts national-weather-service-alerts allows PHP Local File Inclusion.This issue affects National W…
-
High 8.1
WordPress Domnoo theme <= 1.49 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in ApusWP Domnoo domnoo allows PHP Local File Inclusion.This issue affects Domnoo: from n/a through <= 1.49.
-
High 8.1
WordPress BRW plugin <= 1.8.8 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in ovatheme BRW ova-brw allows PHP Local File Inclusion.This issue affects BRW: from n/a through <= 1.8.7.
-
High 8.1
WordPress CityGov theme <= 1.9 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in AncoraThemes CityGov citygov allows PHP Local File Inclusion.This issue affects CityGov: from n/a through <= 1.9.
-
High 8.1
WordPress Zita theme <= 1.6.5 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in themehunk Zita zita allows PHP Local File Inclusion.This issue affects Zita: from n/a through <= 1.6.5.
-
High 8.1
WordPress Samex - Clean, Minimal Shop WooCommerce WordPress Theme <= 2.6 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in snstheme Samex - Clean, Minimal Shop WooCommerce WordPress Theme allows PHP Local File Inclusion. This issue affects Samex - Clean, Minima…
-
High 8.1
WordPress Sofass theme <= 1.3.4 - Local File Inclusion Vulnerability
Improper Control of Filename for Include/Require Statement in PHP Program ('PHP Remote File Inclusion') vulnerability in goalthemes Sofass sofass allows PHP Local File Inclusion.This issue affects Sofass: from n/a through <= 1.3.4.